Início rápido

Este guia abrange todas as funcionalidades do Tailscale:
- Começando — Create your account and install the client
- Como usar uma VPN empresarial — Replace a traditional VPN with a flat private network your whole team can join
- Como usar o acesso remoto seguro — Reach any work machine from anywhere without opening a single firewall port
- Como usar redes site-to-site — Link two office networks together through subnet routers on each side
- Como usar redes multicloud — Put servers from different cloud providers on one flat private network
- Como usar o Kubernetes — Expose cluster services to your tailnet without a public load balancer
- Como usar implantações de Edge e IoT — Manage a fleet of Raspberry Pi boards and sensors from one dashboard
- How to Use Cloud connectivity — Give cloud workloads private access to on-premise databases and hosts
- Como usar a IA para segurança — Keep local models and GPU servers private while your tools still reach them
- How to Use Zero Trust networking — Grant access per user and per device instead of trusting the whole network
Tempo necessário: 5 minutos por filme
Neste guia também: Dicas profissionais | Erros comuns | Solução de problemas | Preços | Alternativas
Por que confiar neste guia?
I have run Tailscale for two years across a Linux machine, a Raspberry Pi, my phone and two cloud servers.
Every step here comes from my own tailnet, not from vendor screenshots.
Tailscale is a mesh VPN built on the WireGuard protocol.
It creates a decentralised network called a tailnet, where dispositivos connect directly to each other.
Most people install it, log in once, then never touch the settings again.
That is a shame, because the good features sit one layer down.
Tutorial de escamas de cauda
This How to Use Tailscale VPN tutorial on how to use Tailscale walks through every feature, from the first install to zero trust access rules.
Escama da cauda
Connect every device you own into one private network in about five minutes. No ports to open, no server to rent, no config files to edit. Free forever for personal use.
Primeiros passos com o Tailscale
Do this once and every feature below becomes available.
It takes about three minutes on any platform.
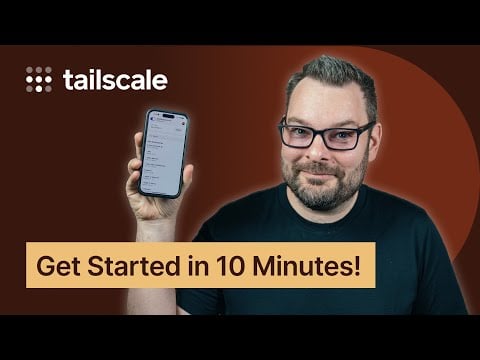
Watch the full walkthrough first:
Agora vamos analisar cada etapa.
Passo 1: Crie sua conta
Go to the Tailscale website and click Get Started.
Sign in with Google, Microsoft, GitHub or Apple instead of making a new password.
✓ Ponto de verificação: The admin console loads with an empty Machines list.
Step 2: Install the Client
Download the app for Windows, macOS, iOS or Android from the site or your app store.
On a Linux machine, run the one-line install script, then escama da cauda para cima.
Apple devices ask for a VPN profile permission on first launch.
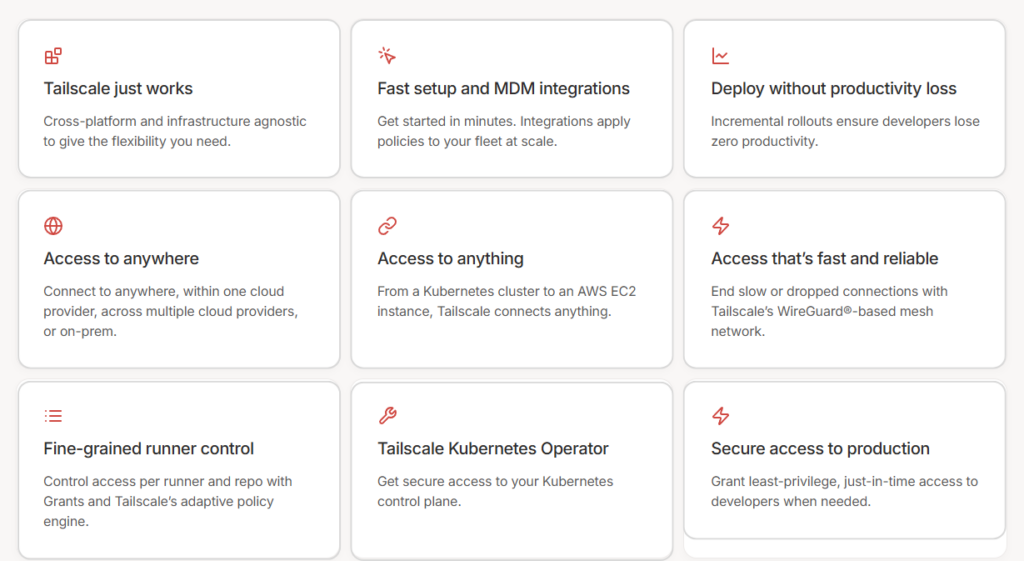
Here’s what you get once the client is running:
✓ Ponto de verificação: Your computer appears in the Machines list with a 100.x.x.x address.
Step 3: Add More Devices
Repeat the install on your phone, your server and any other devices you own.
Once installed, each client finds the others on its own, with nothing to configure.
Every device signed into the same account joins the same tailnet automatically.
Here is how that looked on my own setup:

✅ Concluído: Your tailnet devices can now reach each other by name from anywhere.
Como usar a VPN Tailscale Business
Negócios VPN lets you swap your old corporate VPN for a mesh network that every employee joins in minutes.
Veja como usá-lo passo a passo.
Step 1: Invite Your Users
Open the admin console and send invites by email.
Everyone who signs in with the same domain lands on the same tailnet.
Step 2: Approve Tailnet Devices
Each laptop, phone and server appears in the Machines list after the client installs.
Eis como isso se parece:
✓ Ponto de verificação: Every invited computer shows a 100.x.x.x IP address in the admin console.
Step 3: Set Your Access Policy
Edit the ACL file so each team only reaches the servers it owns.
✅ Resultado: Your team has a private network with no gateway hardware to configure.
💡 Dica profissional: Tailscale uses single-sign-on to authenticate users, so revoking someone in Google Workspace cuts their access imediatamente.
How to Use Tailscale Remote Access
Seguro Acesso remoto lets you reach a work machine from any computer in the world without exposing it to the internet.
Veja como usá-lo passo a passo.
Step 1: Install the Client on Both Ends
Install Tailscale on the office machine and on your laptop.
On Linux the one-line install script does everything.
Step 2: Check Tailscale Status
Correr estado da escama da cauda to confirm both devices are connected.
Eis como isso se parece:
✓ Ponto de verificação: The remote host appears as online with a direct peer connection.
Step 3: Connect by Hostname
SSH or navegar to the device using its MagicDNS name instead of an IP.
✅ Resultado: You can access work files from home without a port forward or public IP.
💡 Dica profissional: Usar tailscale ssh and Tailscale handles the keys for you, so there is no key file to copy around.
Como usar a rede site-to-site da Tailscale
Redes Site-to-Site lets you join two whole networks together instead of installing the app on every machine.
Veja como usá-lo passo a passo.
Step 1: Pick a Gateway Device
Choose one always-on Linux machine at each site.
Step 2: Advertise the Subnet
Run the advertise-routes command with your local range, such as 192.168.1.0/24.
Eis como isso se parece:
✓ Ponto de verificação: Printers and NAS boxes at the far site answer pings from your laptop.
Step 3: Approve the Route
Approve both subnet routers in the admin console under Machines.
✅ Resultado: Two home or office networks now talk as if they sat in one building.
💡 Dica profissional: Enable IP forwarding on the router first, or packets reach the gateway and stop there.
Como usar a rede multi-nuvem da Tailscale
Redes Multi-Nuvem lets you put AWS, GCP and bare-metal servers on the same private network with no peering setup.
Veja como usá-lo passo a passo.
Step 1: Install on Each Server
Add the client to every cloud instance with the one-line script.
Step 2: Use an Auth Key
Generate a reusable auth key so new servers join without a browser login.
Eis como isso se parece:
✓ Ponto de verificação: All cloud hosts appear in one list with 100.x.x.x IP addresses.
Step 3: Tag Your Machines
Apply tags like tag:prod so access rules follow the role, not the person.
✅ Resultado: Your servers communicate across providers without VPC peering or public endpoints.
💡 Dica profissional: Bake the install command into your image so every new node joins the tailnet at boot.
Como usar o Tailscale no Kubernetes
Kubernetes lets you reach internal cluster services from your laptop without a public load balancer.
Veja como usá-lo passo a passo.
Step 1: Install the Operator
Deploy the Tailscale operator into your cluster with Helm.
Step 2: Annotate a Service
Add the Tailscale annotation to any service you want on the tailnet.
Eis como isso se parece:
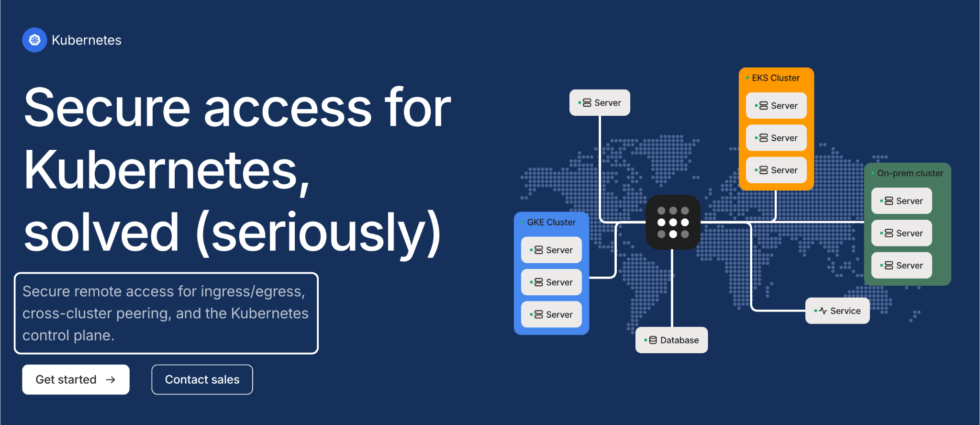
✓ Ponto de verificação: The service shows up as its own device in the Machines list.
Step 3: Open It by Name
Hit the service DNS name from your phone or laptop.
✅ Resultado: Internal dashboards stay off the public internet but remain accessible to your team.
💡 Dica profissional: Use the operator’s API server proxy so kubectl works without a public control plane.
Como usar as implementações de Edge e IoT da Tailscale
Implantações de Edge e IoT lets you manage a Raspberry Pi fleet or a shelf of sensors from one dashboard.
Veja como usá-lo passo a passo.
Step 1: Flash and Install
Install the client on each Raspberry Pi with the standard Linux command.
Step 2: Use Ephemeral Keys
Ephemeral auth keys clean up stale entries when a device goes offline for good.
Eis como isso se parece:
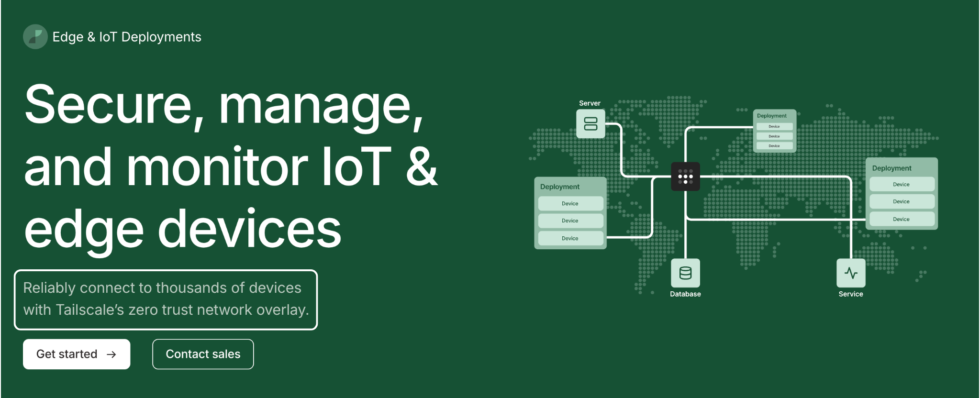
✓ Ponto de verificação: Each board reports online and answers SSH over its tailnet name.
Step 3: Name Every Node
Rename each machine so the hostname tells you where it sits.
✅ Resultado: Field hardware is reachable without static IPs, dynamic DNS or open ports.
💡 Dica profissional: Set a device to never expire, or a remote sensor will drop off after 180 days and need a physical visit.
How to Use Tailscale Cloud connectivity
Cloud connectivity lets you let a cloud app read an on-premise database without a public route.
Veja como usá-lo passo a passo.
Step 1: Route the On-Prem Side
Run a subnet router next to the database and advertise its range.
Step 2: Join the Cloud Workload
Install the client inside the cloud VM or container.
Eis como isso se parece:
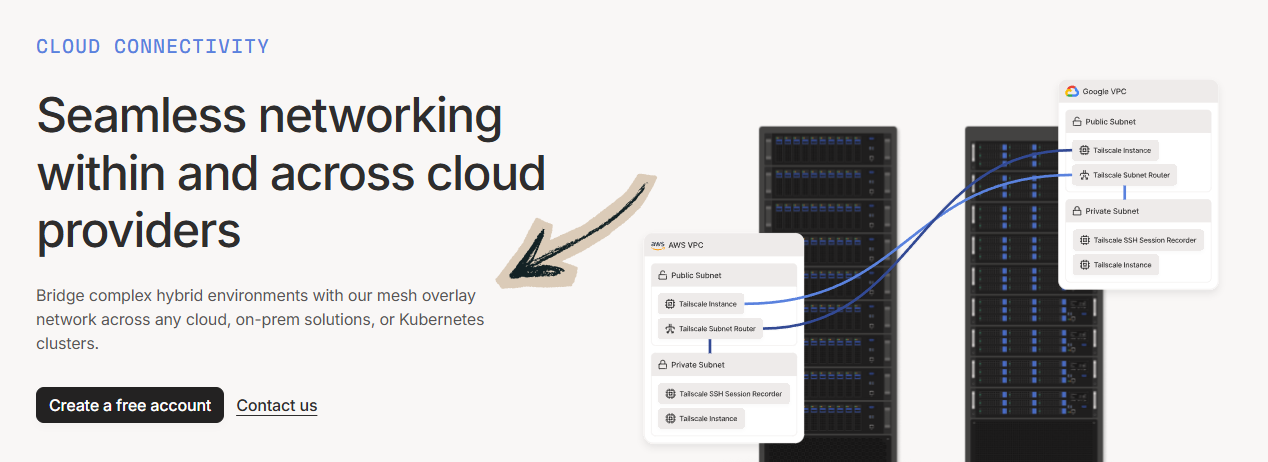
✓ Ponto de verificação: The application connects to the private host by its internal IP.
Step 3: Lock It Down
Write an ACL that allows only that workload to reach the database port.
✅ Resultado: Cloud and on-prem traffic stays encrypted end to end with no bastion host.
💡 Dica profissional: Turn on MagicDNS so the connection string uses a stable name instead of a changing address.
How to Use Tailscale Secure AI
Protegendo a IA lets you keep a GPU box or local model server private while your laptop still reaches it.
Veja como usá-lo passo a passo.
Step 1: Bind Locally
Run the model server on localhost or on the tailnet interface only.
Step 2: Add the GPU Host
Install the client on the GPU machine and confirm it is connected.
Eis como isso se parece:
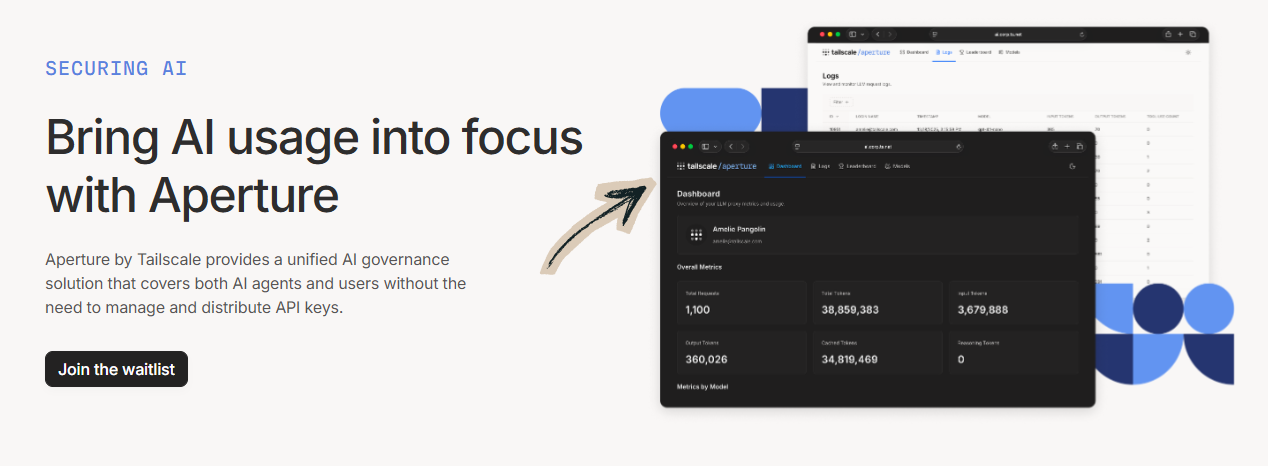
✓ Ponto de verificação: The model answers requests from your laptop and nowhere else.
Step 3: Point Your Tools at It
Use the tailnet hostname as the API endpoint in your app.
✅ Resultado: Your private model is usable from anywhere and invisible to the public internet.
💡 Dica profissional: Share the node with one teammate instead of the whole tailnet when you need a second pair of eyes.
How to Use Tailscale Zero Trust networking
Zero Trust networking lets you grant access per user and per device instead of trusting everyone on the network.
Veja como usá-lo passo a passo.
Step 1: Open the Access Controls
Edit the policy file in the admin console.
Step 2: Write Narrow Rules
Allow each group to reach only the ports it needs.
Eis como isso se parece:
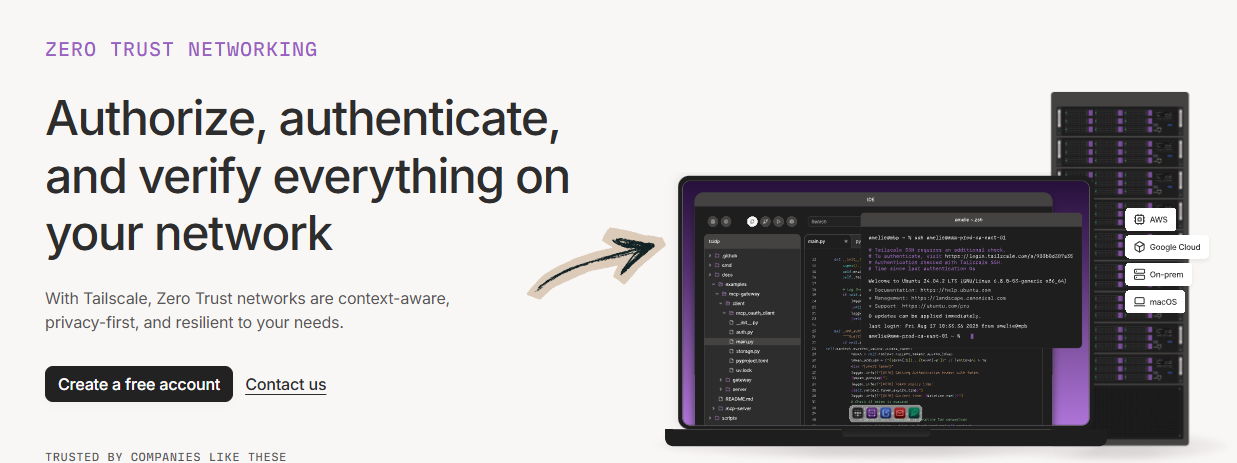
✓ Ponto de verificação: A test account is blocked from a server it should not touch.
Step 3: Require Device Posture
Turn on device approval so new hardware waits for a human check.
✅ Resultado: Access follows identity, so a stolen laptop does not hand over the whole network.
💡 Dica profissional: Use the ACL preview tab before saving, since a bad rule can lock you out of your own machines.
Dicas e Atalhos Profissionais do Tailscale
If you are interested in getting more from your tailnet, start with these.
Handy Commands
| Ação | Comando |
|---|---|
| Check connections | estado da escama da cauda |
| Connect this machine | escama da cauda para cima |
| Send a file | tailscale file cp |
| Test a path | tailscale ping |
Características ocultas que a maioria das pessoas não percebe
- Exit node: Route all internet traffic through one device. For example, a laptop in San Francisco can browse through your home connection. Exit nodes are chosen per client.
- Taildrop: Send files between your own devices without the cloud, straight from the share sheet on a phone.
- MagicDNS: Human-readable hostnames replace raw IP addresses, so
ssh piworks from any client. - Tailscale Serve: Publish a local web server to your tailnet over HTTPS with one command.
Erros comuns a evitar na escama da cauda
Mistake #1: Expecting it to hide your browsing by default
❌ Errado: Installing the app and assuming websites now see a different IP address.
✅ Direita: Only tailnet traffic is routed by default. Pick an exit node if you want your public IP hidden too.
Mistake #2: Forgetting to approve subnet routes
❌ Errado: Running the advertise command, then wondering why the home network is unreachable.
✅ Direita: Approve the route in the admin console and enable IP forwarding on the host.
Mistake #3: Ignoring key expiry
❌ Errado: Leaving a headless server to expire after 180 days and losing remote access.
✅ Direita: Disable key expiry on servers you cannot physically reach.
Solução de problemas da escama de cauda
Problem: Devices connect but the link feels slow
Causa: A direct peer connection failed, so traffic is going through a DERP relay server.
Consertar: Correr verificação de rede de escama de cauda, then open UDP 41641 outbound or turn off strict NAT on the router.
Problem: A machine shows as offline
Causa: The client stopped, or its node key expired.
Consertar: Restart the service, run escama da cauda para cima again and re-authenticate in the browser.
A machine configured months ago sometimes just needs connecting once more.
Problem: Hostnames do not resolve
Causa: MagicDNS is off, or another VPN client is holding the DNS settings.
Consertar: Enable MagicDNS in the admin console and disconnect the other VPN.
📌 Observação: If none of these help, the Tailscale documentation and support team are both quick to answer.
O que é Tailscale?
Escama da cauda is a VPN service that builds a private mesh network between your own machines.
Think of it as a network cable that follows your devices around the world.
It is based on the WireGuard protocol, and its architecture avoids the single point of failure a central VPN server creates.
Traffic takes the shortest path possible, usually a direct peer-to-peer hop, with encrypted packets end to end.
Here is the short version:
Inclui estas características principais:
- VPN empresarial: One tailnet for the whole company, with single-sign-on and admin roles.
- Acesso remoto seguro: Reach a home server or office host without exposing services to the internet.
- Redes ponto a ponto: Subnet routers link entire networks through one gateway device.
- Redes Multi-Nuvem: Servers across providers share one flat set of IP addresses.
- Kubernetes: Cluster services become tailnet devices instead of public endpoints.
- Implantações de Edge e IoT: A Raspberry Pi in the field stays accessible with no open ports.
- Conectividade em nuvem: Cloud workloads reach on-prem hosts over an encrypted path.
- Protegendo a IA: Local model servers stay private while your tools still connect.
- Zero Trust networking: Access rules follow the user and the device, not the network.
For the full breakdown, see our Análise do Tailscale.
Preços de escala de cauda
Here is what Tailscale costs in 2026:
| Plano | Preço | Ideal para |
|---|---|---|
| Pessoal | $0 Grátis para sempre | One user, home network and side projects |
| Personal Plus | US$ 5 por mês | Enthusiasts who want more devices and a few users |
Teste grátis: The Personal plan is free forever, so there is nothing to trial.
Garantia de reembolso: Paid plans are monthly, so you cancel rather than claim a refund.
The Personal plan is free for personal use and covers 20 devices on a single tailnet.
Team plans add advanced SSO, unlimited access control, admin roles and enterprise support.
Here is the pricing page as it stands:
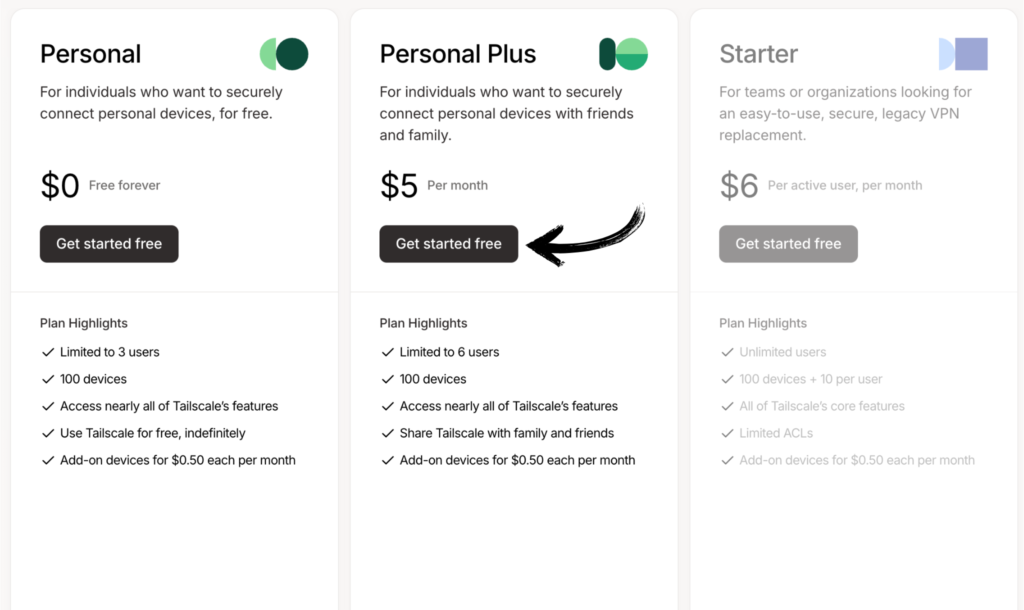
💰 Melhor custo-benefício: Personal — free forever, and enough for a home lab with a Raspberry Pi, a NAS and a laptop.
Tailscale vs. Alternativas
Most tools on this list are privacy VPNs. Tailscale is a networking tool, so compare on the job you need done.
| Ferramenta | Ideal para | Preço | Avaliação |
|---|---|---|---|
| Escama da cauda | Private device networks | $0/mês | ⭐ 4,6 |
| NordVPN | Streaming e privacidade | US$ 12,99/mês | ⭐ 4,7 |
| ExpressVPN | Speed and ease | US$ 12,95/mês | ⭐ 4,6 |
| ProtonVPN | Privacy and free tier | US$ 9,99/mês | ⭐ 4,5 |
| Surfshark VPN | Dispositivos ilimitados | US$ 12,95/mês | ⭐ 4,5 |
| CyberGhost | Servidores de streaming | US$ 12,99/mês | ⭐ 4,3 |
| Acesso privado à internet | Configurable client | $11.95/mo | ⭐ 4,4 |
| PureVPN | Budget plans | $10.95/mo | ⭐ 4,2 |
Escolhas rápidas:
- Melhor no geral: Tailscale — nothing else connects your own machines this quickly.
- Melhor orçamento: Tailscale — the free plan covers most home setups.
- Ideal para iniciantes: ExpressVPN — one button, no networking knowledge needed.
- Best for hiding traffic: ProtonVPN — audited clients and a genuine free tier.
🎯 Alternativas à Tailscale
Looking for Tailscale alternatives? Here are the options worth a look:
- 🚀 NordVPN: Huge server network for streaming and privacy, though it hides your traffic rather than linking your own devices.
- ⭐ ExpressVPN: Fast consumer VPN with apps on nearly every platform, built for location switching instead of private device networking.
- 💰 PureVPN: Budget subscription VPN with a dedicated IP add-on, useful if you only need a hidden public address.
- 💼 Surfshark VPN: Unlimited device connections on one account, a good pick for families who want traffic encryption everywhere.
- 🔒 ProtonVPN: Privacy-first provider with a solid free tier and open-source clients audited by outside firms.
- 👶 PrivadoVPN: Simple free tier with a small monthly dados allowance, aimed at people new to VPN apps.
- 🎯 AdGuard VPN: Pairs traffic encryption with ad blocking, handy on a phone where trackers are the main annoyance.
- 🏢 VirtualShield: Consumer privacy bundle with identity monitoring, sold mainly to households rather than technical users.
- 🔧 StrongVPN: Long-running provider with router support, a fit if you want one device covering the whole home network.
- 📊 AuraVPN: Part of a wider identity protection suite, bundling a VPN with credit and dark web monitoring.
- 🔥 CyberGhost: Streaming-tuned servers and a very long refund window, built for media rather than infrastructure.
- 🧠 VPN McAfee: Bundled with McAfee antivirus, convenient if you already pay for the segurança suíte.
- ⚡ Acesso privado à internet: Configurable client with per-app rules and a no-logs record tested in court.
- 🌟 Mistério: Decentralised node marketplace where users pay for bandwidth from other people’s hardware.
- 🎨 VPN SafeShell: Focused on streaming access with region-specific modes for major platforms.
- 🚀 VPN Oyster: Small provider with cheap long-term plans and a straightforward app on phone and desktop.
Para ver a lista completa, consulte nosso Alternativas à escama de cauda guia.
⚔️ Comparação da escama da cauda
Here is the head-to-head against each one:
- Tailscale vs NordVPN: NordVPN wins for anonymous browsing. Tailscale wins when you want to reach your own machines.
- Tailscale vs ExpressVPN: ExpressVPN is simpler for casual users. Tailscale gives you a real private network.
- Tailscale vs PureVPN: PureVPN is cheaper for streaming. Tailscale is free for personal use and far better for remote access.
- Tailscale vs Surfshark VPN: Surfshark covers more devices per plan. Tailscale connects those devices to each other.
- Tailscale vs ProtonVPN: ProtonVPN is stronger on anonymity. Tailscale is stronger on connectivity between your own servers.
- Tailscale vs PrivadoVPN: PrivadoVPN suits light browsing. Tailscale suits anyone running a home server.
- Tailscale vs AdGuard VPN: AdGuard blocks ads better. Tailscale handles private networks that AdGuard never touches.
- Tailscale vs VirtualShield: VirtualShield targets families. Tailscale targets developers and IT teams.
- Tailscale vs StrongVPN: StrongVPN is easier on an old router. Tailscale gives per-device access rules.
- Tailscale vs AuraVPN: Aura bundles more privacy tools. Tailscale does one job properly.
- Tailscale vs CyberGhost: CyberGhost unblocks more catalogues. Tailscale reaches your NAS and Raspberry Pi.
- Tailscale vs McAfee VPN: McAfee is convenient if bundled. Tailscale is the better standalone network tool.
- Tailscale vs. Acesso Privado à Internet: PIA offers deeper tuning for privacy. Tailscale offers direct peer-to-peer links.
- Escama de Cauda vs. Mistério: Mysterium is more experimental. Tailscale is production-ready for daily work.
- Tailscale vs SafeShell VPN: SafeShell is aimed at viewers. Tailscale is aimed at construtores.
- Tailscale vs Oyster VPN: Oyster costs less monthly. Tailscale costs nothing for a personal tailnet.
Comece a usar o Tailscale agora mesmo
You now know how to use Tailscale across every major feature:
- ✅ VPN para empresas
- ✅ Acesso remoto seguro
- ✅ Rede ponto a ponto
- ✅ Redes Multi-Nuvem
- ✅ Kubernetes
- ✅ Implantações de Edge e IoT
- ✅ Cloud connectivity
- ✅ Protegendo a IA
- ✅ Zero Trust networking
Próximo passo: Install the client on two devices and run estado da escama da cauda.
A maioria das pessoas começa com o Acesso Remoto Seguro.
Leva menos de cinco minutos.
Perguntas frequentes
Como usar o Tailscale na prática?
Create a free account, install the client on two or more devices, and log in with the same account. Each machine gets a 100.x.x.x IP address and connects by name.
O Tailscale é gratuito para uso pessoal?
Yes. The Personal plan is free forever and covers 20 devices on one tailnet. Personal Plus costs $5/per month if you want more devices and a few extra users.
Devo deixar o Tailscale ligado o tempo todo?
Yes, for most people. It only routes tailnet traffic by default, so it barely touches battery or speed unless you turn on an exit node.
O Tailscale oculta meu endereço IP?
Not by default, because normal browsing skips the tailnet. Enable an exit node and your public traffic leaves through that device instead of your own connection.
O Tailscale consegue ver meu tráfego?
No. Packets are encrypted between devices with WireGuard keys. The coordination server handles public key exchange and device lists, never the contents of your connections.
 English
 Spanish
 Chinese
 German
 French
 Arabic
 Russian
 Portuguese
 Japanese
 Korean
 Italian
 Turkish
 Dutch
 Polish
 Indonesian
 Thai
 Vietnamese