クイックスタート

このガイドでは、Tailscaleのすべての機能について説明します。
- はじめる — Create your account and install the client
- ビジネスVPNの使い方 — Replace a traditional VPN with a flat private network your whole team can join
- 安全なリモートアクセスを使用する方法 — Reach any work machine from anywhere without opening a single firewall port
- サイト間ネットワークの使い方 — Link two office networks together through subnet routers on each side
- マルチクラウドネットワークの使い方 — Put servers from different cloud providers on one flat private network
- Kubernetesの使い方 — Expose cluster services to your tailnet without a public load balancer
- Edge & IoT デプロイメントの使い方 — Manage a fleet of Raspberry Pi boards and sensors from one dashboard
- How to Use Cloud connectivity — Give cloud workloads private access to on-premise databases and hosts
- セキュリティAIの使い方 — Keep local models and GPU servers private while your tools still reach them
- How to Use Zero Trust networking — Grant access per user and per device instead of trusting the whole network
所要時間: 各作品につき5分
このガイドには以下の内容も含まれています。 プロのヒント | よくある間違い | トラブルシューティング | 価格 | 代替案
このガイドを信頼する理由
I have run Tailscale for two years across a Linux machine, a Raspberry Pi, my phone and two cloud servers.
Every step here comes from my own tailnet, not from vendor screenshots.
Tailscale is a mesh VPN built on the WireGuard protocol.
It creates a decentralised network called a tailnet, where デバイス connect directly to each other.
Most people install it, log in once, then never touch the settings again.
That is a shame, because the good features sit one layer down.
テールスケールチュートリアル
This How to Use Tailscale VPN tutorial on how to use Tailscale walks through every feature, from the first install to zero trust access rules.
尾秤
Connect every device you own into one private network in about five minutes. No ports to open, no server to rent, no config files to edit. Free forever for personal use.
Tailscale入門
Do this once and every feature below becomes available.
It takes about three minutes on any platform.
Watch the full walkthrough first:
それでは、各ステップを詳しく見ていきましょう。
ステップ1:アカウントを作成する
Go to the Tailscale website and click Get Started.
Sign in with Google, Microsoft, GitHub or Apple instead of making a new password.
✓ チェックポイント: The admin console loads with an empty Machines list.
Step 2: Install the Client
Download the app for Windows, macOS, iOS or Android from the site or your app store.
On a Linux machine, run the one-line install script, then 尾部スケールアップ.
Apple devices ask for a VPN profile permission on first launch.
Here’s what you get once the client is running:
✓ チェックポイント: Your computer appears in the Machines list with a 100.x.x.x address.
Step 3: Add More Devices
Repeat the install on your phone, your server and any other devices you own.
Once installed, each client finds the others on its own, with nothing to configure.
Every device signed into the same account joins the same tailnet automatically.
Here is how that looked on my own setup:

✅ 完了: Your tailnet devices can now reach each other by name from anywhere.
Tailscale Business VPN の使い方
仕事 VPN lets you swap your old corporate VPN for a mesh network that every employee joins in minutes.
以下に、その使用方法をステップごとに説明します。
Step 1: Invite Your Users
Open the admin console and send invites by email.
Everyone who signs in with the same domain lands on the same tailnet.
Step 2: Approve Tailnet Devices
Each laptop, phone and server appears in the Machines list after the client installs.
これがその様子です。
✓ チェックポイント: Every invited computer shows a 100.x.x.x IP address in the admin console.
Step 3: Set Your Access Policy
Edit the ACL file so each team only reaches the servers it owns.
✅ 結果: Your team has a private network with no gateway hardware to configure.
💡 プロのヒント: Tailscale uses single-sign-on to authenticate users, so revoking someone in Google Workspace cuts their access 即座に.
How to Use Tailscale Remote Access
安全な リモートアクセス lets you reach a work machine from any computer in the world without exposing it to the internet.
以下に、その使用方法をステップごとに説明します。
Step 1: Install the Client on Both Ends
Install Tailscale on the office machine and on your laptop.
On Linux the one-line install script does everything.
Step 2: Check Tailscale Status
走る テールスケールの状態 to confirm both devices are connected.
これがその様子です。
✓ チェックポイント: The remote host appears as online with a direct peer connection.
Step 3: Connect by Hostname
SSH or ブラウズ to the device using its MagicDNS name instead of an IP.
✅ 結果: You can access work files from home without a port forward or public IP.
💡 プロのヒント: 使用 tailscale ssh and Tailscale handles the keys for you, so there is no key file to copy around.
Tailscaleのサイト間ネットワークの使い方
サイト間ネットワーク lets you join two whole networks together instead of installing the app on every machine.
以下に、その使用方法をステップごとに説明します。
Step 1: Pick a Gateway Device
Choose one always-on Linux machine at each site.
Step 2: Advertise the Subnet
Run the advertise-routes command with your local range, such as 192.168.1.0/24.
これがその様子です。
✓ チェックポイント: Printers and NAS boxes at the far site answer pings from your laptop.
Step 3: Approve the Route
Approve both subnet routers in the admin console under Machines.
✅ 結果: Two home or office networks now talk as if they sat in one building.
💡 プロのヒント: Enable IP forwarding on the router first, or packets reach the gateway and stop there.
Tailscaleマルチクラウドネットワーキングの使用方法
マルチクラウドネットワーキング lets you put AWS, GCP and bare-metal servers on the same private network with no peering setup.
以下に、その使用方法をステップごとに説明します。
Step 1: Install on Each Server
Add the client to every cloud instance with the one-line script.
Step 2: Use an Auth Key
Generate a reusable auth key so new servers join without a browser login.
これがその様子です。
✓ チェックポイント: All cloud hosts appear in one list with 100.x.x.x IP addresses.
Step 3: Tag Your Machines
Apply tags like tag:prod so access rules follow the role, not the person.
✅ 結果: Your servers communicate across providers without VPC peering or public endpoints.
💡 プロのヒント: Bake the install command into your image so every new node joins the tailnet at boot.
Tailscale Kubernetes の使い方
Kubernetes lets you reach internal cluster services from your laptop without a public load balancer.
以下に、その使用方法をステップごとに説明します。
Step 1: Install the Operator
Deploy the Tailscale operator into your cluster with Helm.
Step 2: Annotate a Service
Add the Tailscale annotation to any service you want on the tailnet.
これがその様子です。
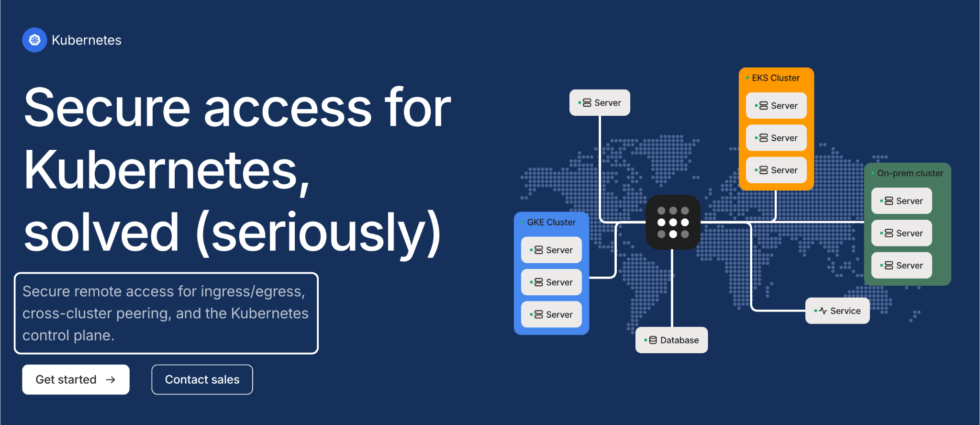
✓ チェックポイント: The service shows up as its own device in the Machines list.
Step 3: Open It by Name
Hit the service DNS name from your phone or laptop.
✅ 結果: Internal dashboards stay off the public internet but remain accessible to your team.
💡 プロのヒント: Use the operator’s API server proxy so kubectl works without a public control plane.
Tailscale EdgeとIoTデプロイメントの使用方法
エッジとIoTの導入 lets you manage a Raspberry Pi fleet or a shelf of sensors from one dashboard.
以下に、その使用方法をステップごとに説明します。
Step 1: Flash and Install
Install the client on each Raspberry Pi with the standard Linux command.
Step 2: Use Ephemeral Keys
Ephemeral auth keys clean up stale entries when a device goes offline for good.
これがその様子です。
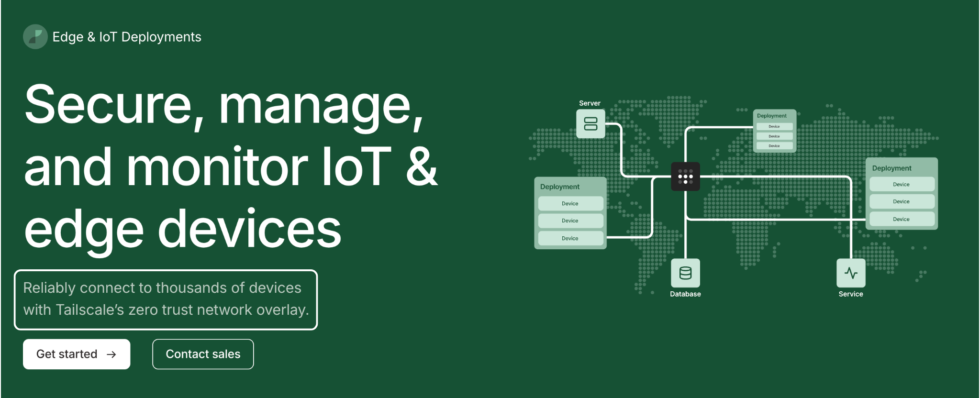
✓ チェックポイント: Each board reports online and answers SSH over its tailnet name.
Step 3: Name Every Node
Rename each machine so the hostname tells you where it sits.
✅ 結果: Field hardware is reachable without static IPs, dynamic DNS or open ports.
💡 プロのヒント: Set a device to never expire, or a remote sensor will drop off after 180 days and need a physical visit.
How to Use Tailscale Cloud connectivity
Cloud connectivity lets you let a cloud app read an on-premise database without a public route.
以下に、その使用方法をステップごとに説明します。
Step 1: Route the On-Prem Side
Run a subnet router next to the database and advertise its range.
Step 2: Join the Cloud Workload
Install the client inside the cloud VM or container.
これがその様子です。
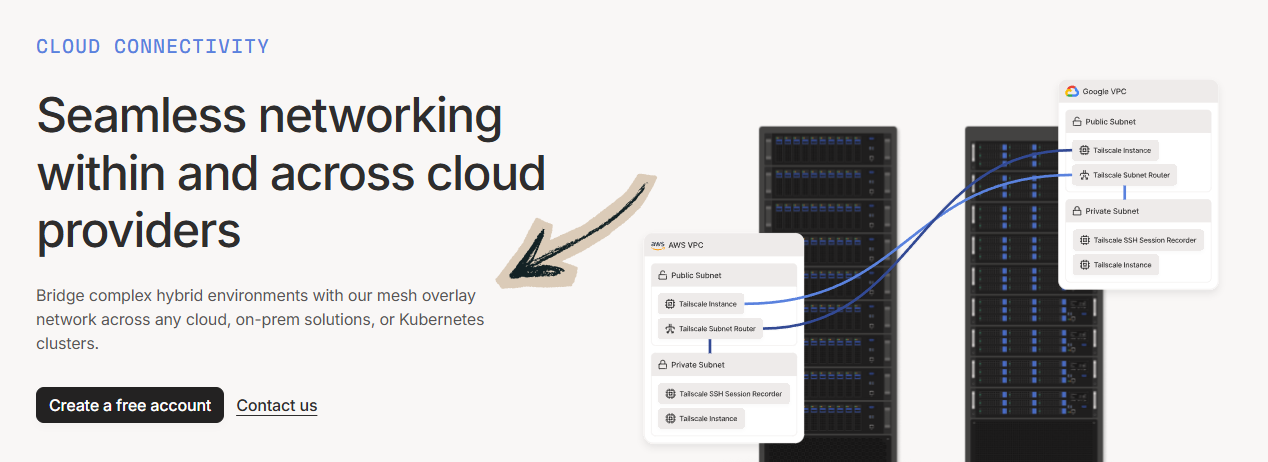
✓ チェックポイント: The application connects to the private host by its internal IP.
Step 3: Lock It Down
Write an ACL that allows only that workload to reach the database port.
✅ 結果: Cloud and on-prem traffic stays encrypted end to end with no bastion host.
💡 プロのヒント: Turn on MagicDNS so the connection string uses a stable name instead of a changing address.
How to Use Tailscale Secure AI
AIのセキュリティ確保 lets you keep a GPU box or local model server private while your laptop still reaches it.
以下に、その使用方法をステップごとに説明します。
Step 1: Bind Locally
Run the model server on localhost or on the tailnet interface only.
Step 2: Add the GPU Host
Install the client on the GPU machine and confirm it is connected.
これがその様子です。
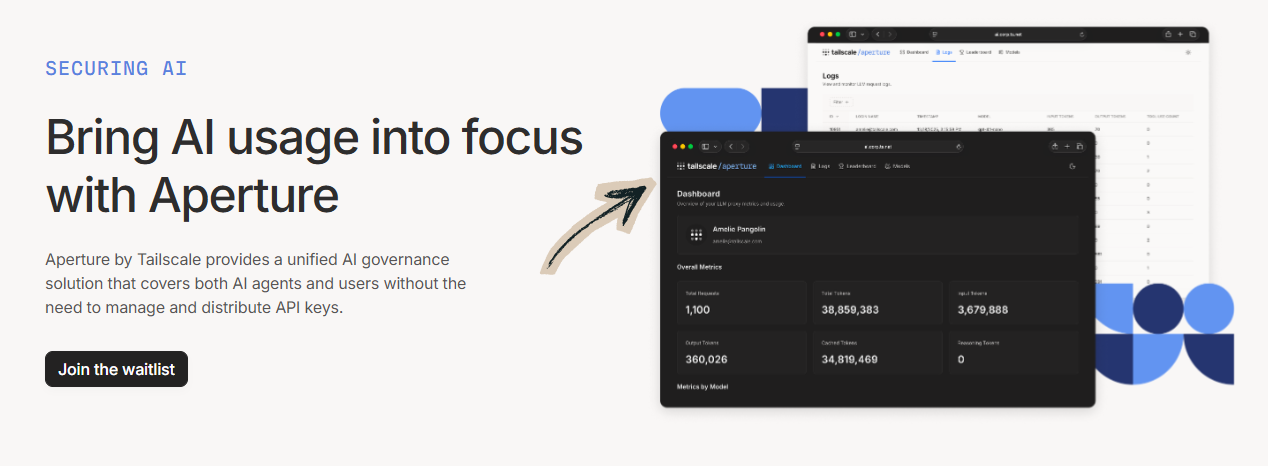
✓ チェックポイント: The model answers requests from your laptop and nowhere else.
Step 3: Point Your Tools at It
Use the tailnet hostname as the API endpoint in your app.
✅ 結果: Your private model is usable from anywhere and invisible to the public internet.
💡 プロのヒント: Share the node with one teammate instead of the whole tailnet when you need a second pair of eyes.
How to Use Tailscale Zero Trust networking
Zero Trust networking lets you grant access per user and per device instead of trusting everyone on the network.
以下に、その使用方法をステップごとに説明します。
Step 1: Open the Access Controls
Edit the policy file in the admin console.
Step 2: Write Narrow Rules
Allow each group to reach only the ports it needs.
これがその様子です。
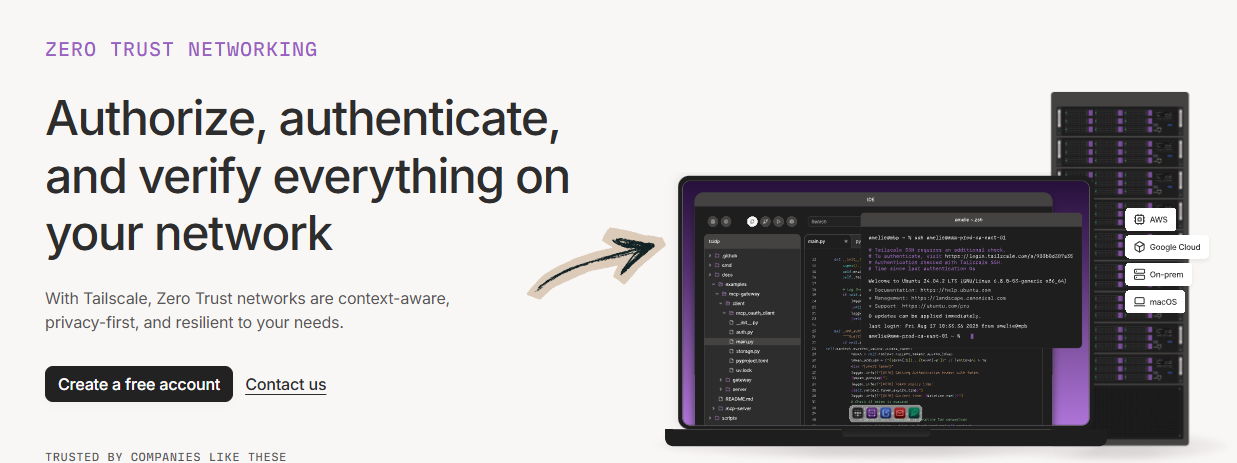
✓ チェックポイント: A test account is blocked from a server it should not touch.
Step 3: Require Device Posture
Turn on device approval so new hardware waits for a human check.
✅ 結果: Access follows identity, so a stolen laptop does not hand over the whole network.
💡 プロのヒント: Use the ACL preview tab before saving, since a bad rule can lock you out of your own machines.
テールスケールのプロ向けヒントとショートカット
If you are interested in getting more from your tailnet, start with these.
Handy Commands
| アクション | 指示 |
|---|---|
| Check connections | テールスケールの状態 |
| Connect this machine | 尾部スケールアップ |
| Send a file | tailscale file cp |
| Test a path | tailscale ping |
ほとんどの人が見逃す隠れた機能
- Exit node: Route all internet traffic through one device. For example, a laptop in San Francisco can browse through your home connection. Exit nodes are chosen per client.
- Taildrop: Send files between your own devices without the cloud, straight from the share sheet on a phone.
- MagicDNS: Human-readable hostnames replace raw IP addresses, so
ssh piworks from any client. - Tailscale Serve: Publish a local web server to your tailnet over HTTPS with one command.
テールスケールでよくある間違いを避ける
Mistake #1: Expecting it to hide your browsing by default
❌ 間違い: Installing the app and assuming websites now see a different IP address.
✅ 右: Only tailnet traffic is routed by default. Pick an exit node if you want your public IP hidden too.
Mistake #2: Forgetting to approve subnet routes
❌ 間違い: Running the advertise command, then wondering why the home network is unreachable.
✅ 右: Approve the route in the admin console and enable IP forwarding on the host.
Mistake #3: Ignoring key expiry
❌ 間違い: Leaving a headless server to expire after 180 days and losing remote access.
✅ 右: Disable key expiry on servers you cannot physically reach.
テールスケールのトラブルシューティング
Problem: Devices connect but the link feels slow
原因: A direct peer connection failed, so traffic is going through a DERP relay server.
修理: 走る テールスケールネットチェック, then open UDP 41641 outbound or turn off strict NAT on the router.
Problem: A machine shows as offline
原因: The client stopped, or its node key expired.
修理: Restart the service, run 尾部スケールアップ again and re-authenticate in the browser.
A machine configured months ago sometimes just needs connecting once more.
Problem: Hostnames do not resolve
原因: MagicDNS is off, or another VPN client is holding the DNS settings.
修理: Enable MagicDNS in the admin console and disconnect the other VPN.
📌 注記: If none of these help, the Tailscale documentation and support team are both quick to answer.
Tailscaleとは何ですか?
尾秤 is a VPN service that builds a private mesh network between your own machines.
Think of it as a network cable that follows your devices around the world.
It is based on the WireGuard protocol, and its architecture avoids the single point of failure a central VPN server creates.
Traffic takes the shortest path possible, usually a direct peer-to-peer hop, with encrypted packets end to end.
Here is the short version:
主な機能は以下のとおりです。
- ビジネスVPN: One tailnet for the whole company, with single-sign-on and admin roles.
- 安全なリモートアクセス: Reach a home server or office host without exposing services to the internet.
- サイト間ネットワーク: Subnet routers link entire networks through one gateway device.
- マルチクラウドネットワーク: Servers across providers share one flat set of IP addresses.
- Kubernetes: Cluster services become tailnet devices instead of public endpoints.
- エッジコンピューティングとIoTの導入事例: A Raspberry Pi in the field stays accessible with no open ports.
- クラウド接続: Cloud workloads reach on-prem hosts over an encrypted path.
- AIのセキュリティ確保: Local model servers stay private while your tools still connect.
- Zero Trust networking: Access rules follow the user and the device, not the network.
For the full breakdown, see our テールスケールのレビュー.
テールスケール価格設定
Here is what Tailscale costs in 2026:
| プラン | 価格 | 最適な用途 |
|---|---|---|
| 個人的 | 永久無料$0 | One user, home network and side projects |
| パーソナルプラス | 月額5ドル | Enthusiasts who want more devices and a few users |
無料トライアル: The Personal plan is free forever, so there is nothing to trial.
返金保証: Paid plans are monthly, so you cancel rather than claim a refund.
The Personal plan is free for personal use and covers 20 devices on a single tailnet.
Team plans add advanced SSO, unlimited access control, admin roles and enterprise support.
Here is the pricing page as it stands:
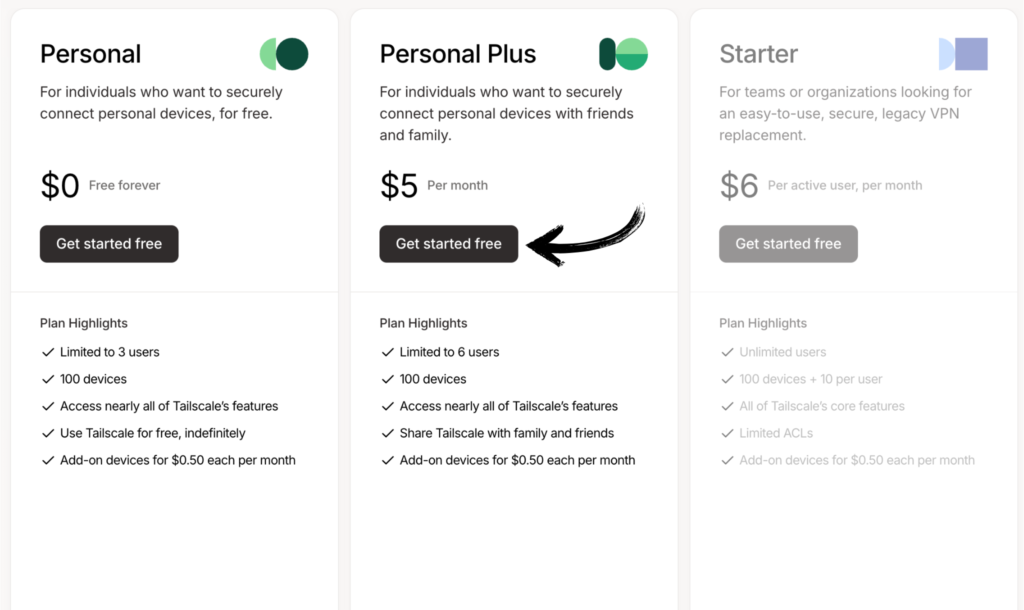
💰 最もお得な価格: Personal — free forever, and enough for a home lab with a Raspberry Pi, a NAS and a laptop.
テールスケールと代替案の比較
Most tools on this list are privacy VPNs. Tailscale is a networking tool, so compare on the job you need done.
| 道具 | 最適な用途 | 価格 | 評価 |
|---|---|---|---|
| 尾秤 | Private device networks | 月額0ドル | ⭐ 4.6 |
| ノードVPN | ストリーミングとプライバシー | 月額12.99ドル | ⭐ 4.7 |
| エクスプレスVPN | Speed and ease | 月額12.95ドル | ⭐ 4.6 |
| プロトンVPN | Privacy and free tier | 月額9.99ドル | ⭐ 4.5 |
| サーフシャークVPN | デバイス数無制限 | 月額12.95ドル | ⭐ 4.5 |
| サイバーゴースト | ストリーミングサーバー | 月額12.99ドル | ⭐ 4.3 |
| プライベートインターネットアクセス | Configurable client | $11.95/mo | ⭐ 4.4 |
| ピュアVPN | Budget plans | $10.95/mo | ⭐ 4.2 |
おすすめ商品:
- 総合ベスト: Tailscale — nothing else connects your own machines this quickly.
- ベスト予算: Tailscale — the free plan covers most home setups.
- 初心者におすすめ: ExpressVPN — one button, no networking knowledge needed.
- Best for hiding traffic: ProtonVPN — audited clients and a genuine free tier.
🎯 テールスケールの代替品
Looking for Tailscale alternatives? Here are the options worth a look:
- 🚀 ノルドVPN: Huge server network for streaming and privacy, though it hides your traffic rather than linking your own devices.
- ⭐ エクスプレスVPN: Fast consumer VPN with apps on nearly every platform, built for location switching instead of private device networking.
- 💰 ピュアVPN: Budget subscription VPN with a dedicated IP add-on, useful if you only need a hidden public address.
- 💼 Surfshark VPN: Unlimited device connections on one account, a good pick for families who want traffic encryption everywhere.
- 🔒 プロトンVPN: Privacy-first provider with a solid free tier and open-source clients audited by outside firms.
- 👶 プライベートVPN: Simple free tier with a small monthly データ allowance, aimed at people new to VPN apps.
- 🎯 アドガードVPN: Pairs traffic encryption with ad blocking, handy on a phone where trackers are the main annoyance.
- 🏢 バーチャルシールド: Consumer privacy bundle with identity monitoring, sold mainly to households rather than technical users.
- 🔧 強力なVPN: Long-running provider with router support, a fit if you want one device covering the whole home network.
- 📊 オーラVPN: Part of a wider identity protection suite, bundling a VPN with credit and dark web monitoring.
- 🔥 サイバーゴースト: Streaming-tuned servers and a very long refund window, built for media rather than infrastructure.
- 🧠 マカフィーVPN: Bundled with McAfee antivirus, convenient if you already pay for the 安全 スイート。
- ⚡ プライベートインターネットアクセス: Configurable client with per-app rules and a no-logs record tested in court.
- 🌟 ミステリウム: Decentralised node marketplace where users pay for bandwidth from other people’s hardware.
- 🎨 SafeShell VPN: Focused on streaming access with region-specific modes for major platforms.
- 🚀 オイスターVPN: Small provider with cheap long-term plans and a straightforward app on phone and desktop.
全リストについては、こちらをご覧ください。 テールスケールの代替品 ガイド。
⚔️ 尾部スケールの比較
Here is the head-to-head against each one:
- Tailscale vs NordVPN: NordVPN wins for anonymous browsing. Tailscale wins when you want to reach your own machines.
- Tailscale vs ExpressVPN: ExpressVPN is simpler for casual users. Tailscale gives you a real private network.
- Tailscale vs PureVPN: PureVPN is cheaper for streaming. Tailscale is free for personal use and far better for remote access.
- TailscaleとSurfshark VPNの比較: Surfshark covers more devices per plan. Tailscale connects those devices to each other.
- Tailscale vs ProtonVPN: ProtonVPN is stronger on anonymity. Tailscale is stronger on connectivity between your own servers.
- Tailscale vs. PrivadoVPN: PrivadoVPN suits light browsing. Tailscale suits anyone running a home server.
- Tailscale vs. AdGuard VPN: AdGuard blocks ads better. Tailscale handles private networks that AdGuard never touches.
- Tailscale vs VirtualShield: VirtualShield targets families. Tailscale targets developers and IT teams.
- Tailscale vs StrongVPN: StrongVPN is easier on an old router. Tailscale gives per-device access rules.
- Tailscale vs AuraVPN: Aura bundles more privacy tools. Tailscale does one job properly.
- テイルスケール対サイバーゴースト: CyberGhost unblocks more catalogues. Tailscale reaches your NAS and Raspberry Pi.
- Tailscale vs McAfee VPN: McAfee is convenient if bundled. Tailscale is the better standalone network tool.
- テールスケール対プライベートインターネットアクセス: PIA offers deeper tuning for privacy. Tailscale offers direct peer-to-peer links.
- テイルスケール対ミステリウム: Mysterium is more experimental. Tailscale is production-ready for daily work.
- TailscaleとSafeShell VPNの比較: SafeShell is aimed at viewers. Tailscale is aimed at 建設業者.
- TailscaleとOyster VPNの比較: Oyster costs less monthly. Tailscale costs nothing for a personal tailnet.
今すぐTailscaleを使い始めましょう
You now know how to use Tailscale across every major feature:
- ✅ ビジネス用VPN
- ✅ 安全なリモートアクセス
- ✅ サイト間ネットワーク
- ✅ マルチクラウドネットワーク
- ✅ Kubernetes
- ✅ エッジコンピューティングとIoTの導入
- ✅ Cloud connectivity
- ✅ AIのセキュリティ確保
- ✅ Zero Trust networking
次のステップ: Install the client on two devices and run テールスケールの状態.
ほとんどの人は、セキュアなリモートアクセスから始めます。
5分もかかりません。
よくある質問
Tailscaleを実際に使うにはどうすればいいですか?
Create a free account, install the client on two or more devices, and log in with the same account. Each machine gets a 100.x.x.x IP address and connects by name.
Tailscaleは個人利用であれば無料ですか?
Yes. The Personal plan is free forever and covers 20 devices on one tailnet. Personal Plus costs $5/per month if you want more devices and a few extra users.
テイルスケールは常にオンにしておくべきでしょうか?
Yes, for most people. It only routes tailnet traffic by default, so it barely touches battery or speed unless you turn on an exit node.
Tailscaleは私のIPアドレスを隠してくれますか?
Not by default, because normal browsing skips the tailnet. Enable an exit node and your public traffic leaves through that device instead of your own connection.
Tailscaleは私のトラフィックを見ることができますか?
No. Packets are encrypted between devices with WireGuard keys. The coordination server handles public key exchange and device lists, never the contents of your connections.
 English
 Spanish
 Chinese
 German
 French
 Arabic
 Russian
 Portuguese
 Japanese
 Korean
 Italian
 Turkish
 Dutch
 Polish
 Indonesian
 Thai
 Vietnamese