Inicio rápido
Esta guía cubre todas las funciones de OpenVPN:
- Empezando — Install openvpn software and make your first vpn connection
- Cómo utilizar el acceso remoto seguro — Lets remote staff reach private servers through one encrypted vpn tunnel.
- Cómo utilizar la comunicación segura de IoT — Keeps cameras, sensors and controllers off the open internet.
- Cree un acceso seguro a las aplicaciones SaaS — Sends SaaS traffic through one fixed address your vendors can allowlist.
- Cómo utilizar la red de sitio a sitio — Joins two offices into one network without paying for leased lines.
- How to Use Enforce Zero Trust Access — Limits each group to the exact systems it needs, nothing more.
- How to Use DNS Security and Content Filtering — Blocks malicious and unwanted domains before anyone loads them.
- Cómo usar la protección SaaS — Shows who touches which cloud app, and blocks the rest.
Tiempo necesario: 5 minutos por función
También en esta guía: Consejos profesionales | Errores comunes | Solución de problemas | Precios | Alternativas
¿Por qué confiar en esta guía?
I’ve run OpenVPN for three years across laptops, routers and a rented Linux box. Every step here comes from my own openvpn installation, not vendor screenshots.
OpenVPN is the openvpn protocol most paid VPN apps quietly run underneath.
You can use it two ways.
Import an ovpn file from a VPN provider, or run your own vpn server.
This guide walks through both, step by step.
Tutorial de OpenVPN
This How to Use OpenVPN tutorial covers install, configuration files, certificates and daily use.
OpenVPN
Run your own encrypted VPN tunnel on hardware you control. OpenVPN Access Server is free for three simultaneous client connections, with no card needed to start.
Introducción a OpenVPN
Antes de usar cualquier función, complete esta configuración inicial.
It takes about ten minutes on a fresh machine.
Step 1: Install OpenVPN
Download the openvpn package for your system from the official site.
On Windows the installer drops files into Program Files and adds the OpenVPN GUI.
Most linux distributions install openvpn with a single apt or dnf command.
✓ Control: Running openvpn –version confirms you have installed openvpn correctly.
Step 2: Get Your Configuration File
Every vpn service hands you an ovpn file, or you build your own.
Most providers ship several ovpn configuration files, one per city.
Self-hosting? Copy the sample server configuration file from the docs folder.
That sample server template already carries sane defaults for a routed vpn.
On Linux, everything lives under /etc/openvpn once you configure openvpn.
That folder holds the server.conf file, your certificate files and keys.
Creating configuration files by hand works, but the sample saves an hour.
Here’s what the working folder looks like:
✓ Control: Your config files sit together in one folder you can find again.
Paso 3: Conéctese por primera vez
Import the profile into OpenVPN Connect, or place it in the client folder.
On Windows, right-click the openvpn gui and run it as administrator.
Then pick the profile and click Connect.
Watch the log window as it scrolls past.
Older guides mention a now authenticated certificate header line.
That only means your openvpn configuration file passed its checks.
✅ Hecho: The log ends with initialization sequence completed. You’re connected.
How to Use OpenVPN Secure Remote Access Tool
Acceso remoto seguro lets you give staff an encrypted vpn tunnel into private servers from any location.
Aquí te mostramos cómo usarlo paso a paso.
Step 1: Add Your Users
Open the Access Server admin panel in your browser.
Add each teammate under User Management and set a password.
Step 2: Send Out the Profile
Click the user, then download their client configuration file.
Share that .ovpn file over a private channel, never email.
Keep all client configuration files in one folder for easy revocation.
Así es como se ve:
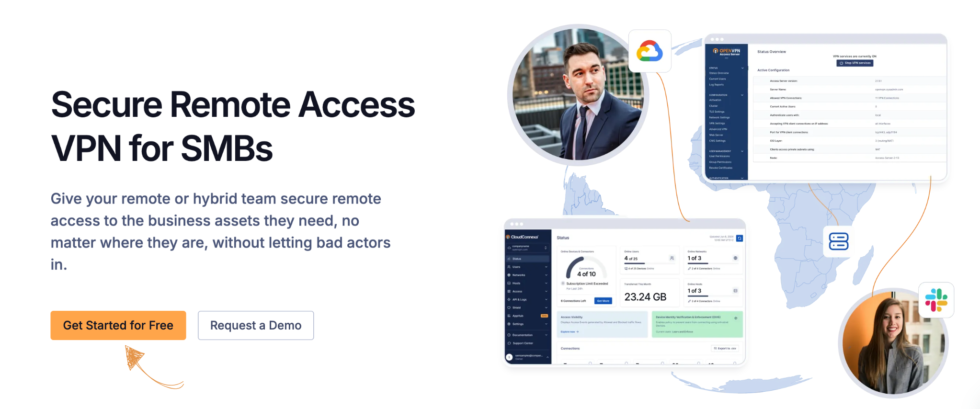
✓ Control: The profile downloads as a single .ovpn file with keys inside.
Paso 3: Conectar y verificar
Import the profile into OpenVPN Connect and hit connect.
Check your public ip address on iplocation.net to confirm the swap.
✅ Resultado: Your team now reaches internal apps over an encrypted openvpn connection.
💡 Consejo profesional: Name each client configuration file after the person, not the device. Revoking access later takes seconds.
How to Use OpenVPN Secure IoT Communicator
Comunicación segura de IoT lets you put cameras, sensors and controllers on a private encrypted link.
Aquí te mostramos cómo usarlo paso a paso.
Step 1: Create a Device Group
Make a separate group for hardware, apart from human users.
Give it read-only access to the subnet it needs.
Step 2: Pin Static Addresses
Use client specific rules to hand each device a fixed address.
Fixed ip addresses make firewall logs readable months later.
Así es como se ve:
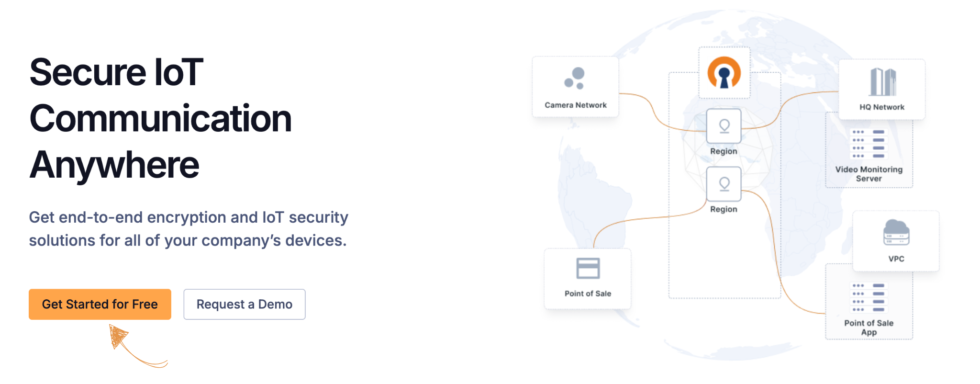
✓ Control: Each device shows the same address on every reconnect.
Step 3: Load the Profile on Device
Copy the ovpn file to the device and start the openvpn service.
Set it to reconnect on boot so nothing drops silently.
✅ Resultado: Your hardware talks home over a private tunnel instead of open ports.
💡 Consejo profesional: Give IoT dispositivos their own client keys. One compromised sensor should never expose the rest.
How to Create OpenVPN Secure Access to SaaS Applications
Cree un acceso seguro a las aplicaciones SaaS lets you route SaaS traffic through one fixed public ip address you can allowlist.
Aquí te mostramos cómo usarlo paso a paso.
Step 1: Note Your Gateway Address
Find the public ip address of your vpn server machine.
That single address becomes your front door to every SaaS vendor.
Step 2: Allowlist It With Vendors
Paste the address into each SaaS admin panel under IP restrictions.
Most tools call this trusted IP ranges or network allowlisting.
Así es como se ve:
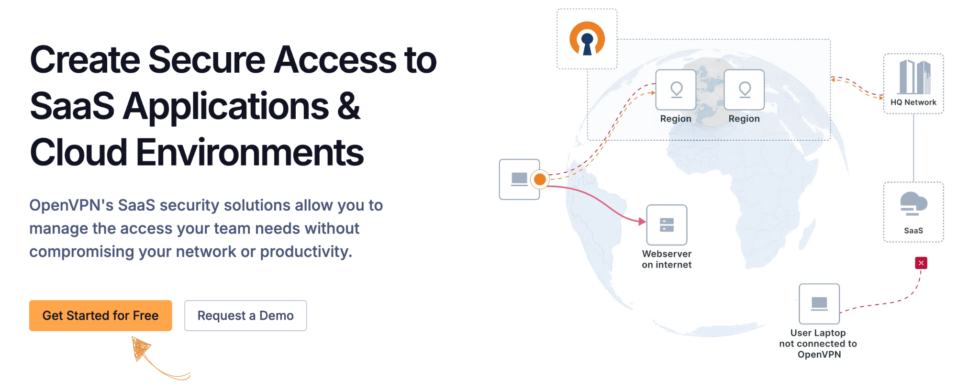
✓ Control: Logging in from outside the tunnel now gets refused.
Step 3: Force Traffic Through the Tunnel
Turn on redirect gateway so all traffic uses the vpn connection.
Split tunnelling here would break the allowlist you just built.
✅ Resultado: Stolen passwords stop working unless the attacker is inside your vpn.
💡 Consejo profesional: Keep a second gateway address on standby. If your host rotates addresses, logins break instantáneamente.
Cómo usar OpenVPN para redes de sitio a sitio
Redes de sitio a sitio lets you join two offices into one private network without leased lines.
Aquí te mostramos cómo usarlo paso a paso.
Step 1: Pick Non-Overlapping Subnets
Each site needs its own range, such as 10.8.1.0 and 10.8.2.0.
Matching ranges are the number one cause of routing failures.
Step 2: Set the Gateway Role
Mark one site as gateway inside the openvpn server configuration.
This runs a routed vpn, which suits office links better than bridging.
Así es como se ve:
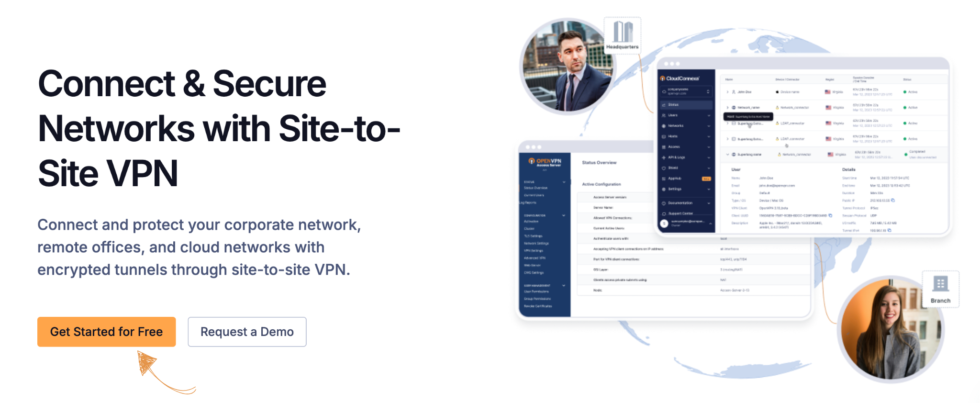
✓ Control: A ping from one office reaches a printer at the other.
Step 3: Push the Routes
Add push route lines so each side learns the other subnet.
Restart openvpn on both ends to apply the change.
✅ Resultado: Both offices share files and printers as if they sat in one building.
💡 Consejo profesional: Document the subnet map before you build. Future you will thank present you during outages.
How to Use OpenVPN Enforce Zero Trust Access
Implementar el acceso de confianza cero lets you limit every user group to the exact systems it needs.
Aquí te mostramos cómo usarlo paso a paso.
Step 1: Map Groups to Systems
List which teams truly need billing, staging or production access.
Most people need far less than they currently hold.
Step 2: Write the Access Rules
Set per-group subnet rules in the admin panel or the server config file.
Deny everything first, then open only what the group requires.
Así es como se ve:
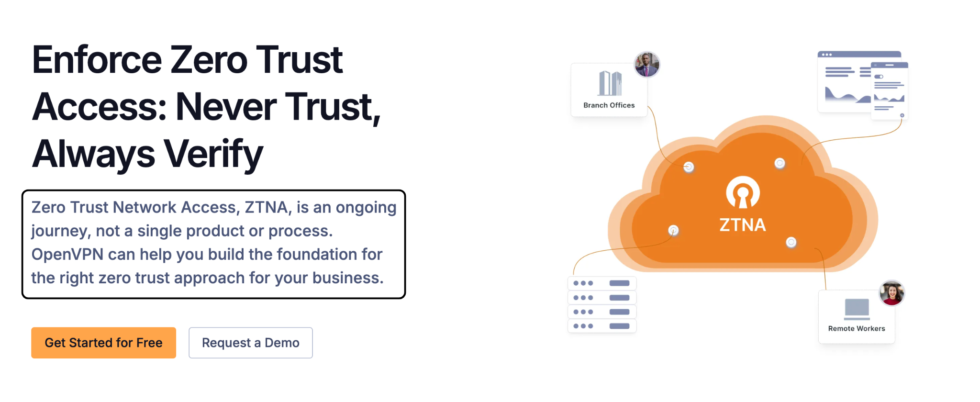
✓ Control: A test account can reach its own subnet and nothing else.
Step 3: Add a Second Factor
Turn on multi-factor authentication alongside your server and client certificates.
Certificates prove the machine, MFA proves the person.
✅ Resultado: One stolen laptop no longer opens your whole network.
💡 Consejo profesional: Review group rules every quarter. Access creep happens quietly as people change roles.
How to Use OpenVPN DNS Security and Content Filtering
DNS Seguridad and Content Filtering lets you block malicious domains before anyone on the tunnel loads them.
Aquí te mostramos cómo usarlo paso a paso.
Step 1: Push Your Resolvers
Add push dhcp-option DNS lines to send dns servers to clients.
Without this, laptops leak lookups to whatever café router they meet.
Step 2: Choose Filter Categories
Switch on categories such as malware, phishing and adult content.
Start narrow, then widen once support tickets stay quiet.
Así es como se ve:
✓ Control: Your resolver appears in the client log, not the local router.
Step 3: Test a Blocked Domain
Visit a known test domain from a connected client machine.
A block page confirms filtering runs inside the tunnel.
✅ Resultado: Every connected device inherits the same filtering, even on hotel Wi-Fi.
💡 Consejo profesional: Whitelist your own domains first. Filters love to block internal tools on day one.
How to Use OpenVPN SaaS Protector
Protección SaaS lets you watch and lock down how your team signs into cloud apps.
Aquí te mostramos cómo usarlo paso a paso.
Step 1: Turn On Access Logging
Enable connection logging for client connections in the admin panel.
You want names, times and addresses, not just totals.
Step 2: Review Weekly Patterns
Scan for logins at odd hours or from unexpected countries.
Odd patterns show up long before a breach does.
Así es como se ve:
✓ Control: The log shows each session with a user name attached.
Step 3: Cut Off Stale Accounts
Revoke the client certificate the day someone leaves.
Revocation beats password changes because the key file dies too.
✅ Resultado: You can answer who accessed what, and when, in under a minute.
💡 Consejo profesional: Export logs monthly to cold storage. Auditors ask for history your dashboard no longer keeps.
Consejos y atajos profesionales para OpenVPN
After three years of configuring openvpn, these are the habits that stuck.
This is the terminal view I keep open while testing:

Commands Worth Memorising
| Acción | Atajo |
|---|---|
| Connect from terminal | sudo openvpn –config client.ovpn |
| Restart openvpn service | sudo systemctl restart openvpn@server |
| Watch the live log | sudo journalctl -fu openvpn@server |
| Check the tunnel interface | ip addr show tun0 |
Características ocultas que la mayoría de la gente pasa por alto
- Client specific rules: Drop a file named after the client into the ccd folder. Configuring client specific rules lets you pin routes per user.
- Interfaz de gestión: Add a management line to the server config file, then telnet in to watch client connect events live.
- The vars file: Edit vars inside the easy-rsa directory once, and every certificate signing request inherits your details automatically.
- Offline signing: Keep the ca private key on an air-gapped machine, or a dedicated key server. Your server key then never travels.
Errores comunes que debes evitar con OpenVPN
Mistake #1: Emailing the Private Key
❌ Incorrecto: Sending certificate files and the private key as an email attachment.
✅ Derecha: Hand over key files through a administrador de contraseñas or an encrypted share.
Mistake #2: Copying a Config Without Reading It
❌ Incorrecto: Pasting a random openvpn server configuration file from a forum thread.
✅ Derecha: Start from the official sample configuration files, then change one line at a time.
Mistake #3: Forgetting IP Forwarding
❌ Incorrecto: Building the tunnel, then wondering why no website loads through it.
✅ Derecha: Turn on ip forwarding and add the firewall rule before you blame the openvpn configuration.
Solución de problemas de OpenVPN
Problema: Falló el protocolo de enlace TLS.
Causa: The client cannot reach the vpn server, or tls authentication keys do not match.
Arreglar: Confirm port 1194 UDP is open, then check both ends share the same tls-crypt key.
Problem: Connected but No Internet
Causa: Traffic enters the tunnel and stops, usually missing routing or dns servers.
Arreglar: Enable ip forwarding, add a NAT rule, and push a resolver to clients.
Problem: Certificate Verify Failed
Causa: The server certificate expired, or the ca server signed with a different root.
Arreglar: Reissue the client certificate from the same CA, then restart openvpn on both sides.
📌 Nota: Si ninguna de estas soluciones resuelve su problema, póngase en contacto con el soporte técnico de OpenVPN.
¿Qué es OpenVPN?
OpenVPN is open-source vpn software that builds an encrypted tunnel using SSL/TLS.
Think of it as a private hallway between two buildings on a public street.
The same openvpn software runs as both vpn server and vpn client.
Mira este breve resumen:
Incluye estas características clave:
- Acceso remoto seguro: Lets remote staff reach private servers through one encrypted vpn tunnel.
- Comunicación segura de IoT: Keeps cameras, sensors and controllers off the open internet.
- Create Secure Access to SaaS Applications: Sends SaaS traffic through one fixed address your vendors can allowlist.
- Redes de sitio a sitio: Joins two offices into one network without paying for leased lines.
- Enforce Zero Trust Access: Limits each group to the exact systems it needs, nothing more.
- DNS Security and Content Filtering: Blocks malicious and unwanted domains before anyone loads them.
- Protección SaaS: Shows who touches which cloud app, and blocks the rest.
It relies on a public key infrastructure, so both sides check each other before trusting anything.
That means server and client certificates, signed by one authority you control.
Para una revisión completa, consulte nuestra Análisis de OpenVPN.
Precios de OpenVPN
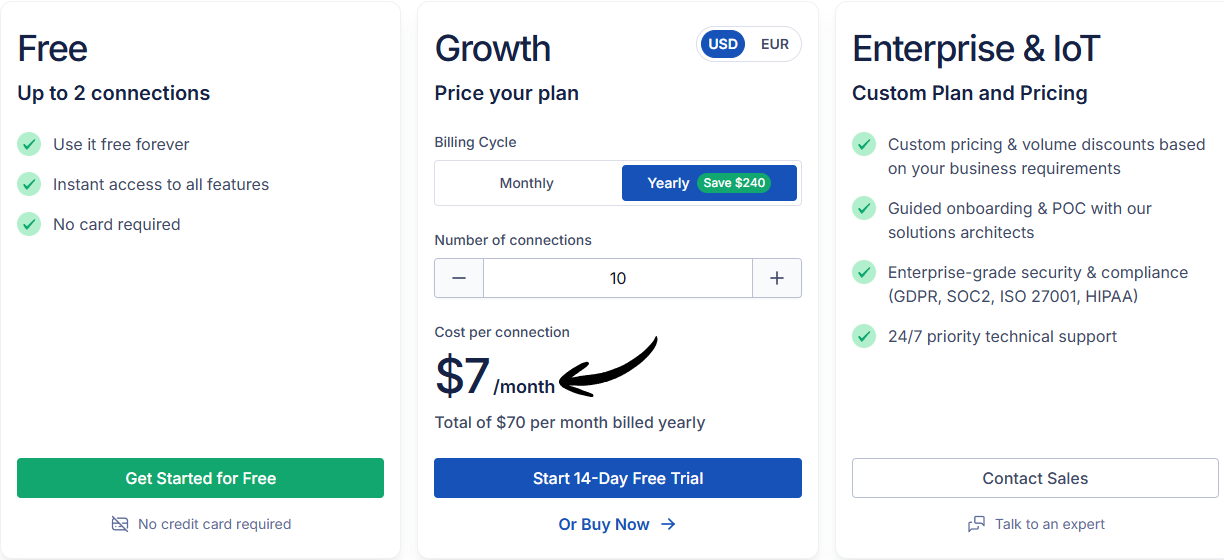
Esto es lo que costará OpenVPN en 2026:
| Plan | Precio | Mejor para |
|---|---|---|
| Gratis | $0 | Home labs and up to three connections |
| Crecimiento | $7/mes | Small teams that need more seats |
| Empresa | Costumbre | Large fleets and compliance needs |
Prueba gratuita: Yes — the community edition stays free forever on your own hardware.
Garantía de devolución de dinero: Not needed on Free; paid plans bill per connection each month.
💰 Mejor relación calidad-precio: Free — a $5 cloud box plus the openvpn package covers most households.
OpenVPN frente a alternativas
How does OpenVPN compare? Here is the landscape:
| Herramienta | Mejor para | Precio | Clasificación |
|---|---|---|---|
| OpenVPN | Self-hosted control | $7/mes | ⭐ 4.6 |
| NordVPN | Speed and server count | $3.39/mes | ⭐ 4.8 |
| ExpressVPN | Simple apps everywhere | $4.99/mes | ⭐ 4.7 |
| PureVPN | Budget long-term plans | $2.11/mo | ⭐ 4.3 |
| SurfsharkVPN | Dispositivos ilimitados | $2.19/mes | ⭐ 4.6 |
| ProtonVPN | Privacy and free tier | $4.49/mes | ⭐ 4.7 |
| PrivadoVPN | Entrada de pago más barata | $1.11/mes | ⭐ 4.1 |
| CyberGhost | Servidores de streaming | $2.19/mes | ⭐ 4.4 |
Selecciones rápidas:
- Mejor en general: OpenVPN — you own the vpn server machine and every key.
- Mejor presupuesto: PrivadoVPN — cheapest way to skip running your own server.
- Ideal para principiantes: ExpressVPN — one button, no configuration file to touch.
- Lo mejor para la privacidad: ProtonVPN — audited apps and a usable free plan.
🎯 Alternativas a OpenVPN
¿Buscas alternativas a OpenVPN? Aquí tienes las mejores opciones:
- 🚀 Nordvpn: Huge server network and NordLynx speeds, though you never touch the underlying config file.
- 🌟 ExpressVPN: The most forgiving apps on every platform, with its own Lightway protocol instead of openvpn.
- 💰 PureVPN: Long multi-year deals at low monthly cost, plus optional dedicated ip addresses.
- ⚡ SurfsharkVPN: Unlimited simultaneous devices on one account, which suits families and multiple clients.
- 🔒 ProtonVPN: Swiss privacy law, open-source apps and a free tier with no datos cap.
- 👶 PrivadoVPN: Very cheap entry pricing and a simple interface for first-time vpn client users.
- 🎯 CyberGhost: Servers labelled by streaming service, so you skip the guesswork entirely.
Para ver la lista completa, consulte nuestra Alternativas a OpenVPN guía.
⚔️ Comparativa de OpenVPN
Here is how OpenVPN stacks up against each competitor:
- OpenVPN vs Nordvpn: Nord wins on speed and setup time. OpenVPN wins if you want the server under your own roof.
- OpenVPN frente a ExpressVPN: Express is easier for travel. OpenVPN costs nothing once your box runs.
- OpenVPN frente a PureVPN: PureVPN is cheaper per month. OpenVPN gives full control of logging and keys.
- OpenVPN vs SurfsharkVPN: Tiburón de surf covers unlimited devices. OpenVPN covers unlimited devices too, if you self-host.
- OpenVPN frente a ProtonVPN: Proton is the better ready-made privacy vpn service. OpenVPN is the better toolkit.
- OpenVPN vs PrivadoVPN: Privado wins on price alone. OpenVPN wins on transparency and auditoría senderos.
- OpenVPN vs CyberGhost: CyberGhost is built for streaming. OpenVPN is built for infrastructure.
Empiece a usar OpenVPN ahora
Aprendiste a usar todas las funciones principales de OpenVPN:
- ✅ Acceso remoto seguro
- ✅ Comunicación segura de IoT
- ✅ Create Secure Access to SaaS Applications
- ✅ Redes de sitio a sitio
- ✅ Enforce Zero Trust Access
- ✅ DNS Security and Content Filtering
- ✅ Protección SaaS
Siguiente paso: Elige una función y pruébala ahora.
La mayoría de la gente empieza con el acceso remoto seguro.
Tarda menos de cinco minutos.
Preguntas frecuentes
¿Cómo puedo usar OpenVPN como VPN?
Install the openvpn client, import an ovpn file from your vpn provider, then connect. All traffic then travels inside an encrypted tunnel to the vpn server.
¿Cómo inicio OpenVPN?
On Windows, launch the OpenVPN GUI as administrator and pick your profile from the system tray applet. On Linux, run sudo systemctl start openvpn@server.
¿Puedo usar OpenVPN gratis?
Yes. The community edition is free and open source. Access Server is also free for three simultaneous client connections, which covers most home setups.
¿Cómo usar OpenVPN en Windows?
Install openvpn software, copy your .ovpn configuration file into the config folder inside Program Files, then right-click the tray icon and choose Connect.
¿Cuál es la diferencia entre VPN y OpenVPN?
A VPN is the general idea of a private tunnel. OpenVPN is one specific openvpn protocol and program that creates that tunnel using SSL/TLS.
 English
 Spanish
 Chinese
 German
 French
 Arabic
 Russian
 Portuguese
 Japanese
 Korean
 Italian
 Turkish
 Dutch
 Polish
 Indonesian
 Thai
 Vietnamese