빠른 시작
이 가이드에서는 OpenVPN의 모든 기능을 다룹니다.
- 시작하기 — Install openvpn software and make your first vpn connection
- 안전한 원격 접속 사용 방법 — Lets remote staff reach private servers through one encrypted vpn tunnel.
- 안전한 IoT 통신 사용 방법 — Keeps cameras, sensors and controllers off the open internet.
- SaaS 애플리케이션에 대한 안전한 액세스 권한 생성 — Sends SaaS traffic through one fixed address your vendors can allowlist.
- 사이트 간 네트워킹 사용 방법 — Joins two offices into one network without paying for leased lines.
- How to Use Enforce Zero Trust Access — Limits each group to the exact systems it needs, nothing more.
- How to Use DNS Security and Content Filtering — Blocks malicious and unwanted domains before anyone loads them.
- SaaS 보호 기능을 사용하는 방법 — Shows who touches which cloud app, and blocks the rest.
소요 시간: 각 작품당 5분
이 가이드에는 다음 내용도 포함되어 있습니다. 프로 팁 | 흔히 저지르는 실수 | 문제 해결 | 가격 | 대안
이 가이드를 신뢰해야 하는 이유
I’ve run OpenVPN for three years across laptops, routers and a rented Linux box. Every step here comes from my own openvpn installation, not vendor screenshots.
OpenVPN is the openvpn protocol most paid VPN apps quietly run underneath.
You can use it two ways.
Import an ovpn file from a VPN provider, or run your own vpn server.
This guide walks through both, step by step.
OpenVPN 튜토리얼
This How to Use OpenVPN tutorial covers install, configuration files, certificates and daily use.
오픈VPN
Run your own encrypted VPN tunnel on hardware you control. OpenVPN Access Server is free for three simultaneous client connections, with no card needed to start.
OpenVPN 시작하기
Loading...
It takes about ten minutes on a fresh machine.
Step 1: Install OpenVPN
Download the openvpn package for your system from the official site.
On Windows the installer drops files into Program Files and adds the OpenVPN GUI.
Most linux distributions install openvpn with a single apt or dnf command.
✓ 검문소: Running openvpn –version confirms you have installed openvpn correctly.
Step 2: Get Your Configuration File
Every vpn service hands you an ovpn file, or you build your own.
Most providers ship several ovpn configuration files, one per city.
Self-hosting? Copy the sample server configuration file from the docs folder.
That sample server template already carries sane defaults for a routed vpn.
On Linux, everything lives under /etc/openvpn once you configure openvpn.
That folder holds the server.conf file, your certificate files and keys.
Creating configuration files by hand works, but the sample saves an hour.
Here’s what the working folder looks like:
✓ 검문소: Your config files sit together in one folder you can find again.
3단계: 최초 연결
Import the profile into OpenVPN Connect, or place it in the client folder.
On Windows, right-click the openvpn gui and run it as administrator.
Then pick the profile and click Connect.
Watch the log window as it scrolls past.
Older guides mention a now authenticated certificate header line.
That only means your openvpn configuration file passed its checks.
✅ 완료: The log ends with initialization sequence completed. You’re connected.
How to Use OpenVPN Secure Remote Access Tool
안전한 원격 접속 lets you give staff an encrypted vpn tunnel into private servers from any location.
다음은 단계별 사용 방법입니다.
Step 1: Add Your Users
Open the Access Server admin panel in your browser.
Add each teammate under User Management and set a password.
Step 2: Send Out the Profile
Click the user, then download their client configuration file.
Share that .ovpn file over a private channel, never email.
Keep all client configuration files in one folder for easy revocation.
이것이 어떤 모습인지 보여드리겠습니다:
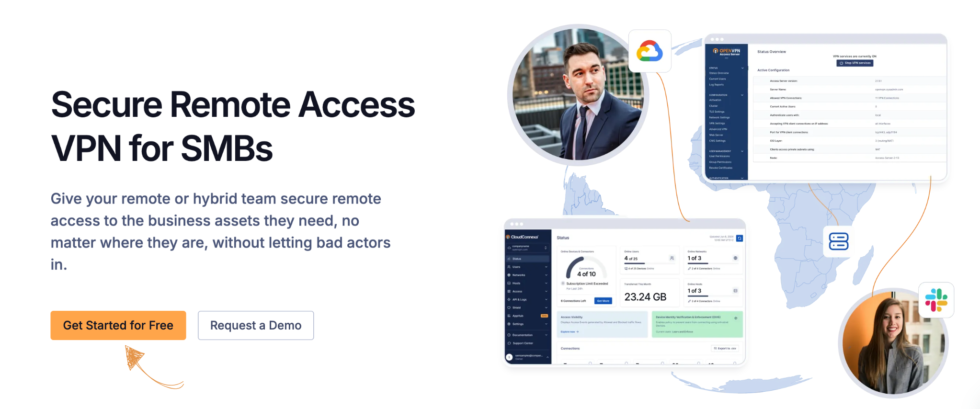
✓ 검문소: The profile downloads as a single .ovpn file with keys inside.
3단계: 연결 및 확인
Import the profile into OpenVPN Connect and hit connect.
Check your public ip address on iplocation.net to confirm the swap.
✅ 결과: Your team now reaches internal apps over an encrypted openvpn connection.
💡 꿀팁: Name each client configuration file after the person, not the device. Revoking access later takes seconds.
How to Use OpenVPN Secure IoT Communicator
안전한 IoT 통신 lets you put cameras, sensors and controllers on a private encrypted link.
다음은 단계별 사용 방법입니다.
Step 1: Create a Device Group
Make a separate group for hardware, apart from human users.
Give it read-only access to the subnet it needs.
Step 2: Pin Static Addresses
Use client specific rules to hand each device a fixed address.
Fixed ip addresses make firewall logs readable months later.
이것이 어떤 모습인지 보여드리겠습니다:
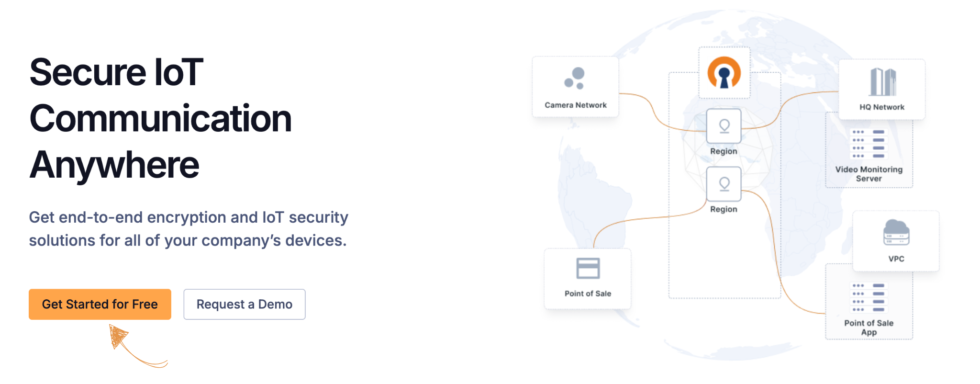
✓ 검문소: Each device shows the same address on every reconnect.
Step 3: Load the Profile on Device
Copy the ovpn file to the device and start the openvpn service.
Set it to reconnect on boot so nothing drops silently.
✅ 결과: Your hardware talks home over a private tunnel instead of open ports.
💡 꿀팁: Give IoT 기기 their own client keys. One compromised sensor should never expose the rest.
How to Create OpenVPN Secure Access to SaaS Applications
SaaS 애플리케이션에 대한 안전한 액세스 권한 생성 lets you route SaaS traffic through one fixed public ip address you can allowlist.
다음은 단계별 사용 방법입니다.
Step 1: Note Your Gateway Address
Find the public ip address of your vpn server machine.
That single address becomes your front door to every SaaS vendor.
Step 2: Allowlist It With Vendors
Paste the address into each SaaS admin panel under IP restrictions.
Most tools call this trusted IP ranges or network allowlisting.
이것이 어떤 모습인지 보여드리겠습니다:
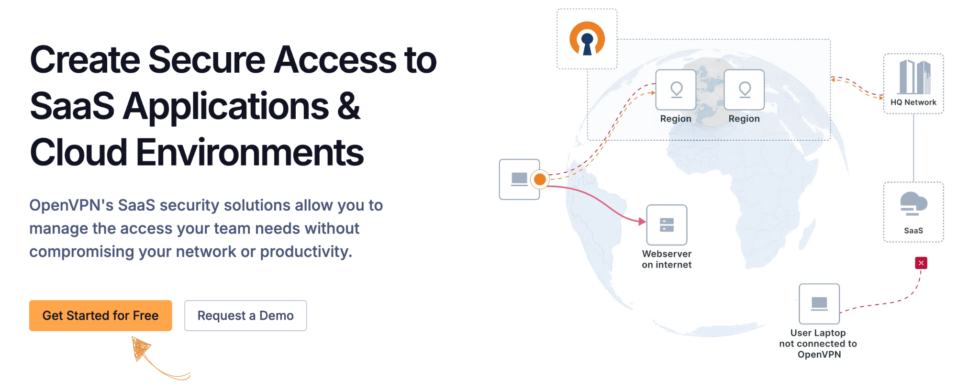
✓ 검문소: Logging in from outside the tunnel now gets refused.
Step 3: Force Traffic Through the Tunnel
Turn on redirect gateway so all traffic uses the vpn connection.
Split tunnelling here would break the allowlist you just built.
✅ 결과: Stolen passwords stop working unless the attacker is inside your vpn.
💡 꿀팁: Keep a second gateway address on standby. If your host rotates addresses, logins break 곧.
OpenVPN 사이트 간 네트워킹 사용 방법
사이트 간 네트워킹 lets you join two offices into one private network without leased lines.
다음은 단계별 사용 방법입니다.
Step 1: Pick Non-Overlapping Subnets
Each site needs its own range, such as 10.8.1.0 and 10.8.2.0.
Matching ranges are the number one cause of routing failures.
Step 2: Set the Gateway Role
Mark one site as gateway inside the openvpn server configuration.
This runs a routed vpn, which suits office links better than bridging.
이것이 어떤 모습인지 보여드리겠습니다:
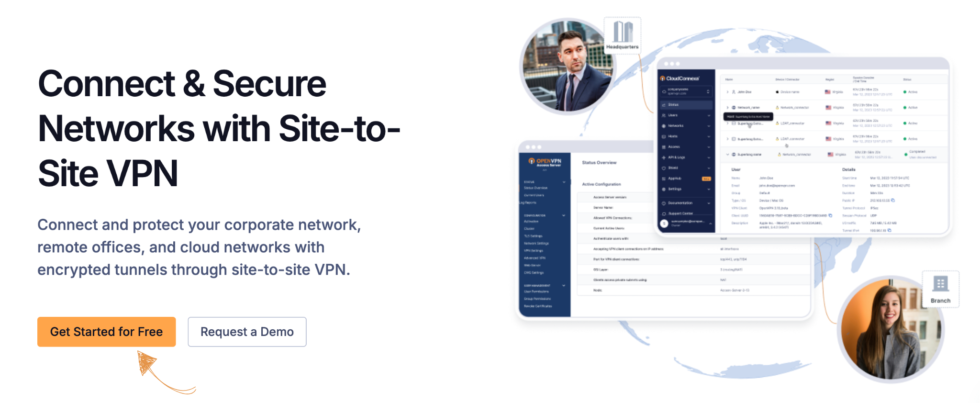
✓ 검문소: A ping from one office reaches a printer at the other.
Step 3: Push the Routes
Add push route lines so each side learns the other subnet.
Restart openvpn on both ends to apply the change.
✅ 결과: Both offices share files and printers as if they sat in one building.
💡 꿀팁: Document the subnet map before you build. Future you will thank present you during outages.
How to Use OpenVPN Enforce Zero Trust Access
제로 트러스트 액세스 시행 lets you limit every user group to the exact systems it needs.
다음은 단계별 사용 방법입니다.
Step 1: Map Groups to Systems
List which teams truly need billing, staging or production access.
Most people need far less than they currently hold.
Step 2: Write the Access Rules
Set per-group subnet rules in the admin panel or the server config file.
Deny everything first, then open only what the group requires.
이것이 어떤 모습인지 보여드리겠습니다:
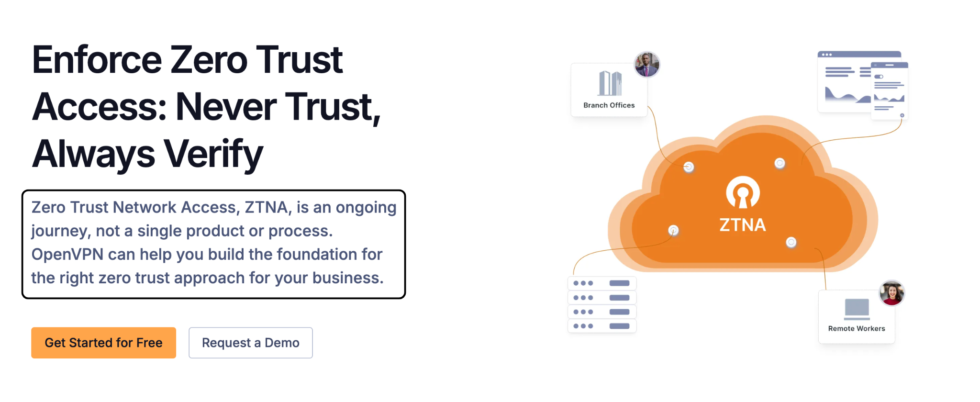
✓ 검문소: A test account can reach its own subnet and nothing else.
Step 3: Add a Second Factor
Turn on multi-factor authentication alongside your server and client certificates.
Certificates prove the machine, MFA proves the person.
✅ 결과: One stolen laptop no longer opens your whole network.
💡 꿀팁: Review group rules every quarter. Access creep happens quietly as people change roles.
How to Use OpenVPN DNS Security and Content Filtering
DNS 보안 and Content Filtering lets you block malicious domains before anyone on the tunnel loads them.
다음은 단계별 사용 방법입니다.
Step 1: Push Your Resolvers
Add push dhcp-option DNS lines to send dns servers to clients.
Without this, laptops leak lookups to whatever café router they meet.
Step 2: Choose Filter Categories
Switch on categories such as malware, phishing and adult content.
Start narrow, then widen once support tickets stay quiet.
이것이 어떤 모습인지 보여드리겠습니다:
✓ 검문소: Your resolver appears in the client log, not the local router.
Step 3: Test a Blocked Domain
Visit a known test domain from a connected client machine.
A block page confirms filtering runs inside the tunnel.
✅ 결과: Every connected device inherits the same filtering, even on 호텔 와이파이.
💡 꿀팁: Whitelist your own domains first. Filters love to block internal tools on day one.
How to Use OpenVPN SaaS Protector
SaaS 보호 lets you watch and lock down how your team signs into cloud apps.
다음은 단계별 사용 방법입니다.
Step 1: Turn On Access Logging
Enable connection logging for client connections in the admin panel.
You want names, times and addresses, not just totals.
Step 2: Review Weekly Patterns
Scan for logins at odd hours or from unexpected countries.
Odd patterns show up long before a breach does.
이것이 어떤 모습인지 보여드리겠습니다:
✓ 검문소: The log shows each session with a user name attached.
Step 3: Cut Off Stale Accounts
Revoke the client certificate the day someone leaves.
Revocation beats password changes because the key file dies too.
✅ 결과: You can answer who accessed what, and when, in under a minute.
💡 꿀팁: Export logs monthly to cold storage. Auditors ask for history your dashboard no longer keeps.
OpenVPN 전문가 팁 및 바로가기
After three years of configuring openvpn, these are the habits that stuck.
This is the terminal view I keep open while testing:

Commands Worth Memorising
| 행동 | 지름길 |
|---|---|
| Connect from terminal | sudo openvpn –config client.ovpn |
| Restart openvpn service | sudo systemctl restart openvpn@server |
| Watch the live log | sudo journalctl -fu openvpn@server |
| Check the tunnel interface | ip addr show tun0 |
대부분의 사람들이 놓치는 숨겨진 기능들
- Client specific rules: Drop a file named after the client into the ccd folder. Configuring client specific rules lets you pin routes per user.
- 관리 인터페이스: Add a management line to the server config file, then telnet in to watch client connect events live.
- The vars file: Edit vars inside the easy-rsa directory once, and every certificate signing request inherits your details automatically.
- Offline signing: Keep the ca private key on an air-gapped machine, or a dedicated key server. Your server key then never travels.
OpenVPN에서 흔히 저지르는 실수, 피해야 할 것들
Mistake #1: Emailing the Private Key
❌ 틀림: Sending certificate files and the private key as an email attachment.
✅ 오른쪽: Hand over key files through a 비밀번호 관리자 or an encrypted share.
Mistake #2: Copying a Config Without Reading It
❌ 틀림: Pasting a random openvpn server configuration file from a forum thread.
✅ 오른쪽: Start from the official sample configuration files, then change one line at a time.
Mistake #3: Forgetting IP Forwarding
❌ 틀림: Building the tunnel, then wondering why no website loads through it.
✅ 오른쪽: Turn on ip forwarding and add the firewall rule before you blame the openvpn configuration.
OpenVPN 문제 해결
문제: TLS 핸드셰이크 실패
원인: The client cannot reach the vpn server, or tls authentication keys do not match.
고치다: Confirm port 1194 UDP is open, then check both ends share the same tls-crypt key.
Problem: Connected but No Internet
원인: Traffic enters the tunnel and stops, usually missing routing or dns servers.
고치다: Enable ip forwarding, add a NAT rule, and push a resolver to clients.
Problem: Certificate Verify Failed
원인: The server certificate expired, or the ca server signed with a different root.
고치다: Reissue the client certificate from the same CA, then restart openvpn on both sides.
📌 메모: 이러한 방법으로도 문제가 해결되지 않으면 OpenVPN 지원팀에 문의하십시오.
OpenVPN이란 무엇인가요?
오픈VPN is open-source vpn software that builds an encrypted tunnel using SSL/TLS.
Think of it as a private hallway between two buildings on a public street.
The same openvpn software runs as both vpn server and vpn client.
이 간단한 개요를 시청하세요:
이 제품에는 다음과 같은 주요 기능이 포함되어 있습니다.
- 안전한 원격 접속: Lets remote staff reach private servers through one encrypted vpn tunnel.
- 안전한 IoT 통신: Keeps cameras, sensors and controllers off the open internet.
- Create Secure Access to SaaS Applications: Sends SaaS traffic through one fixed address your vendors can allowlist.
- 사이트 간 네트워킹: Joins two offices into one network without paying for leased lines.
- Enforce Zero Trust Access: Limits each group to the exact systems it needs, nothing more.
- DNS Security and Content Filtering: Blocks malicious and unwanted domains before anyone loads them.
- SaaS 보호: Shows who touches which cloud app, and blocks the rest.
It relies on a public key infrastructure, so both sides check each other before trusting anything.
That means server and client certificates, signed by one authority you control.
자세한 내용은 저희 웹사이트를 참조하세요. OpenVPN 리뷰.
OpenVPN 가격
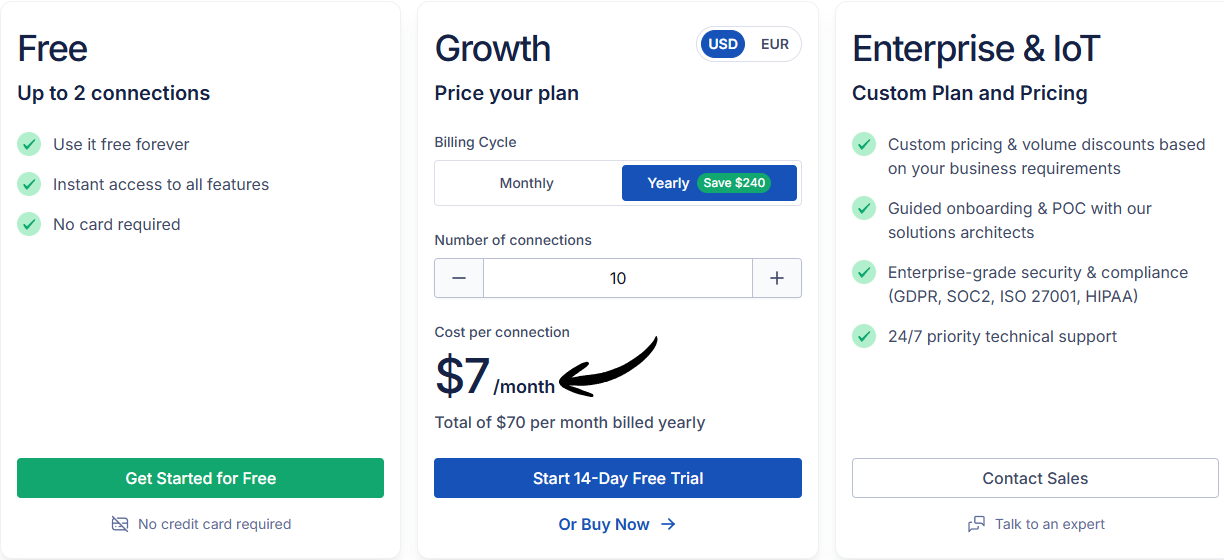
다음은 2026년 OpenVPN 비용입니다.
| 계획 | 가격 | 가장 적합한 대상 |
|---|---|---|
| 무료 | $0 | Home labs and up to three connections |
| 성장 | 월 7달러 | Small teams that need more seats |
| 기업 | 관습 | Large fleets and compliance needs |
무료 체험: Yes — the community edition stays free forever on your own hardware.
환불 보장: Not needed on Free; paid plans bill per connection each month.
💰 최고의 가성비: Free — a $5 cloud box plus the openvpn package covers most households.
OpenVPN과 대안 VPN 비교
How does OpenVPN compare? Here is the landscape:
| 도구 | 가장 적합한 대상 | 가격 | 평가 |
|---|---|---|---|
| 오픈VPN | Self-hosted control | 월 7달러 | ⭐ 4.6 |
| NordVPN | Speed and server count | 월 3.39달러 | ⭐ 4.8 |
| ExpressVPN | Simple apps everywhere | 월 4.99달러 | ⭐ 4.7 |
| 퓨어VPN | Budget long-term plans | $2.11/mo | ⭐ 4.3 |
| 서프샤크VPN | 무제한 기기 | 월 2.19달러 | ⭐ 4.6 |
| 프로톤VPN | Privacy and free tier | 월 4.49달러 | ⭐ 4.7 |
| PrivadoVPN | 가장 저렴한 유료 입장권 | 월 1.11달러 | ⭐ 4.1 |
| 사이버고스트 | 스트리밍 서버 | 월 2.19달러 | ⭐ 4.4 |
빠른 추천:
- 종합 최고상: OpenVPN — you own the vpn server machine and every key.
- 최고의 가성비: PrivadoVPN — cheapest way to skip running your own server.
- 초보자에게 가장 적합: ExpressVPN — one button, no configuration file to touch.
- 개인 정보 보호에 가장 적합한 것: ProtonVPN — audited apps and a usable free plan.
🎯 OpenVPN 대안
OpenVPN 대안을 찾고 계신가요? 다음은 최고의 옵션들입니다.
- 🚀 Nordvpn: Huge server network and NordLynx speeds, though you never touch the underlying config file.
- 🌟 ExpressVPN: The most forgiving apps on every platform, with its own Lightway protocol instead of openvpn.
- 💰 PureVPN: Long multi-year deals at low monthly cost, plus optional dedicated ip addresses.
- ⚡ SurfsharkVPN: Unlimited simultaneous devices on one account, which suits families and multiple clients.
- 🔒 프로톤VPN: Swiss privacy law, open-source apps and a free tier with no 데이터 cap.
- 👶 PrivadoVPN: Very cheap entry pricing and a simple interface for first-time vpn client users.
- 🎯 사이버고스트: Servers labelled by streaming service, so you skip the guesswork entirely.
전체 목록은 다음을 참조하세요. OpenVPN 대안 가이드.
⚔️ OpenVPN 비교
Here is how OpenVPN stacks up against each competitor:
- OpenVPN vs Nordvpn: Nord wins on speed and setup time. OpenVPN wins if you want the server under your own roof.
- OpenVPN vs ExpressVPN: Express is easier for travel. OpenVPN costs nothing once your box runs.
- OpenVPN vs PureVPN: PureVPN is cheaper per month. OpenVPN gives full control of logging and keys.
- OpenVPN vs SurfsharkVPN: 서프샤크 covers unlimited devices. OpenVPN covers unlimited devices too, if you self-host.
- OpenVPN vs ProtonVPN: Proton is the better ready-made privacy vpn service. OpenVPN is the better toolkit.
- OpenVPN과 PrivadoVPN 비교: Privado wins on price alone. OpenVPN wins on transparency and 심사 트레일.
- OpenVPN vs CyberGhost: CyberGhost is built for streaming. OpenVPN is built for infrastructure.
지금 바로 OpenVPN을 사용해 보세요
여러분은 OpenVPN의 주요 기능을 모두 사용하는 방법을 배웠습니다.
- ✅ 안전한 원격 접속
- ✅ 안전한 IoT 통신
- ✅ Create Secure Access to SaaS Applications
- ✅ 사이트 간 네트워킹
- ✅ Enforce Zero Trust Access
- ✅ DNS Security and Content Filtering
- ✅ SaaS 보호
다음 단계: 기능 하나를 선택해서 지금 바로 사용해 보세요.
대부분의 사람들은 보안 원격 액세스부터 시작합니다.
5분도 채 걸리지 않습니다.
자주 묻는 질문
OpenVPN을 VPN으로 사용하는 방법은 무엇인가요?
Install the openvpn client, import an ovpn file from your vpn provider, then connect. All traffic then travels inside an encrypted tunnel to the vpn server.
OpenVPN은 어떻게 시작하나요?
On Windows, launch the OpenVPN GUI as administrator and pick your profile from the system tray applet. On Linux, run sudo systemctl start openvpn@server.
OpenVPN을 무료로 사용할 수 있나요?
Yes. The community edition is free and open source. Access Server is also free for three simultaneous client connections, which covers most home setups.
Windows에서 OpenVPN을 사용하는 방법은 무엇인가요?
Install openvpn software, copy your .ovpn configuration file into the config folder inside Program Files, then right-click the tray icon and choose Connect.
VPN과 OpenVPN의 차이점은 무엇인가요?
A VPN is the general idea of a private tunnel. OpenVPN is one specific openvpn protocol and program that creates that tunnel using SSL/TLS.
 English
 Spanish
 Chinese
 German
 French
 Arabic
 Russian
 Portuguese
 Japanese
 Korean
 Italian
 Turkish
 Dutch
 Polish
 Indonesian
 Thai
 Vietnamese