เริ่มต้นใช้งานอย่างรวดเร็ว

คู่มือนี้ครอบคลุมคุณสมบัติทุกอย่างของ Tailscale:
- เริ่มต้นใช้งาน — Create your account and install the client
- วิธีใช้งาน VPN สำหรับธุรกิจ — Replace a traditional VPN with a flat private network your whole team can join
- วิธีใช้งานการเข้าถึงระยะไกลที่ปลอดภัย — Reach any work machine from anywhere without opening a single firewall port
- วิธีใช้งานเครือข่ายระหว่างไซต์ — Link two office networks together through subnet routers on each side
- วิธีใช้งานเครือข่ายมัลติคลาวด์ — Put servers from different cloud providers on one flat private network
- วิธีใช้งาน Kubernetes — Expose cluster services to your tailnet without a public load balancer
- วิธีใช้งาน Edge และ IoT Deployment — Manage a fleet of Raspberry Pi boards and sensors from one dashboard
- How to Use Cloud connectivity — Give cloud workloads private access to on-premise databases and hosts
- วิธีใช้งาน AI รักษาความปลอดภัย — Keep local models and GPU servers private while your tools still reach them
- How to Use Zero Trust networking — Grant access per user and per device instead of trusting the whole network
ระยะเวลาที่ใช้: แต่ละฟีเจอร์ใช้เวลา 5 นาที
นอกจากนี้ในคู่มือนี้ยังมี: เคล็ดลับสำหรับมืออาชีพ | ข้อผิดพลาดที่พบบ่อย | การแก้ไขปัญหา | ความละเอียด | ตัวเลือกต่าง ๆ
เหตุใดจึงควรเชื่อถือคู่มือนี้
I have run Tailscale for two years across a Linux machine, a Raspberry Pi, my phone and two cloud servers.
Every step here comes from my own tailnet, not from vendor screenshots.
Tailscale is a mesh VPN built on the WireGuard protocol.
It creates a decentralised network called a tailnet, where อุปกรณ์ connect directly to each other.
Most people install it, log in once, then never touch the settings again.
That is a shame, because the good features sit one layer down.
บทช่วยสอนเกี่ยวกับเกล็ดหาง
This How to Use Tailscale VPN tutorial on how to use Tailscale walks through every feature, from the first install to zero trust access rules.
เกล็ดหาง
Connect every device you own into one private network in about five minutes. No ports to open, no server to rent, no config files to edit. Free forever for personal use.
เริ่มต้นใช้งาน Tailscale กันเถอะ
Do this once and every feature below becomes available.
It takes about three minutes on any platform.
Watch the full walkthrough first:
ทีนี้เรามาอธิบายแต่ละขั้นตอนกัน
ขั้นตอนที่ 1: สร้างบัญชีของคุณ
Go to the Tailscale website and click Get Started.
Sign in with Google, Microsoft, GitHub or Apple instead of making a new password.
✓ ด่าน: The admin console loads with an empty Machines list.
Step 2: Install the Client
Download the app for Windows, macOS, แอป iOS or Android from the site or your app store.
On a Linux machine, run the one-line install script, then เกล็ดหางขึ้น.
Apple devices ask for a VPN profile permission on first launch.
Here’s what you get once the client is running:
✓ ด่าน: Your computer appears in the Machines list with a 100.x.x.x address.
Step 3: Add More Devices
Repeat the install on your phone, your server and any other devices you own.
Once installed, each client finds the others on its own, with nothing to configure.
Every device signed into the same account joins the same tailnet automatically.
Here is how that looked on my own setup:

✅ เสร็จเรียบร้อยแล้ว: Your tailnet devices can now reach each other by name from anywhere.
วิธีใช้งาน Tailscale Business VPN
ธุรกิจ VPN lets you swap your old corporate VPN for a mesh network that every employee joins in minutes.
นี่คือวิธีการใช้งานทีละขั้นตอน
Step 1: Invite Your Users
Open the admin console and send invites by email.
Everyone who signs in with the same domain lands on the same tailnet.
Step 2: Approve Tailnet Devices
Each laptop, phone and server appears in the Machines list after the client installs.
นี่คือหน้าตาของมัน:
✓ ด่าน: Every invited computer shows a 100.x.x.x IP address in the admin console.
Step 3: Set Your Access Policy
Edit the ACL file so each team only reaches the servers it owns.
✅ ผลลัพธ์: Your team has a private network with no gateway hardware to configure.
💡 เคล็ดลับสำหรับมืออาชีพ: Tailscale uses single-sign-on to authenticate users, so revoking someone in Google Workspace cuts their access ทันที.
How to Use Tailscale Remote Access
ปลอดภัย การเข้าถึงระยะไกล lets you reach a work machine from any computer in the world without exposing it to the internet.
นี่คือวิธีการใช้งานทีละขั้นตอน
Step 1: Install the Client on Both Ends
Install Tailscale on the office machine and on your laptop.
On Linux the one-line install script does everything.
Step 2: Check Tailscale Status
วิ่ง สถานะเกล็ดหาง to confirm both devices are connected.
นี่คือหน้าตาของมัน:
✓ ด่าน: The remote host appears as online with a direct peer connection.
Step 3: Connect by Hostname
SSH or เรียกดู to the device using its MagicDNS name instead of an IP.
✅ ผลลัพธ์: You can access work files from home without a port forward or public IP.
💡 เคล็ดลับสำหรับมืออาชีพ: ใช้ tailscale ssh and Tailscale handles the keys for you, so there is no key file to copy around.
วิธีใช้งานระบบเครือข่ายแบบ Site-to-Site ของ Tailscale
การเชื่อมต่อเครือข่ายระหว่างไซต์ lets you join two whole networks together instead of installing the app on every machine.
นี่คือวิธีการใช้งานทีละขั้นตอน
Step 1: Pick a Gateway Device
Choose one always-on Linux machine at each site.
Step 2: Advertise the Subnet
Run the advertise-routes command with your local range, such as 192.168.1.0/24.
นี่คือหน้าตาของมัน:
✓ ด่าน: Printers and NAS boxes at the far site answer pings from your laptop.
Step 3: Approve the Route
Approve both subnet routers in the admin console under Machines.
✅ ผลลัพธ์: Two home or office networks now talk as if they sat in one building.
💡 เคล็ดลับสำหรับมืออาชีพ: Enable IP forwarding on the router first, or packets reach the gateway and stop there.
วิธีใช้งานระบบเครือข่ายมัลติคลาวด์ของ Tailscale
เครือข่ายมัลติคลาวด์ lets you put AWS, GCP and bare-metal servers on the same private network with no peering setup.
นี่คือวิธีการใช้งานทีละขั้นตอน
Step 1: Install on Each Server
Add the client to every cloud instance with the one-line script.
Step 2: Use an Auth Key
Generate a reusable auth key so new servers join without a browser login.
นี่คือหน้าตาของมัน:
✓ ด่าน: All cloud hosts appear in one list with 100.x.x.x IP addresses.
Step 3: Tag Your Machines
Apply tags like tag:prod so access rules follow the role, not the person.
✅ ผลลัพธ์: Your servers communicate across providers without VPC peering or public endpoints.
💡 เคล็ดลับสำหรับมืออาชีพ: Bake the install command into your image so every new node joins the tailnet at boot.
วิธีใช้งาน Tailscale Kubernetes
คูเบอร์เน็ตส์ lets you reach internal cluster services from your laptop without a public load balancer.
นี่คือวิธีการใช้งานทีละขั้นตอน
Step 1: Install the Operator
Deploy the Tailscale operator into your cluster with Helm.
Step 2: Annotate a Service
Add the Tailscale annotation to any service you want on the tailnet.
นี่คือหน้าตาของมัน:
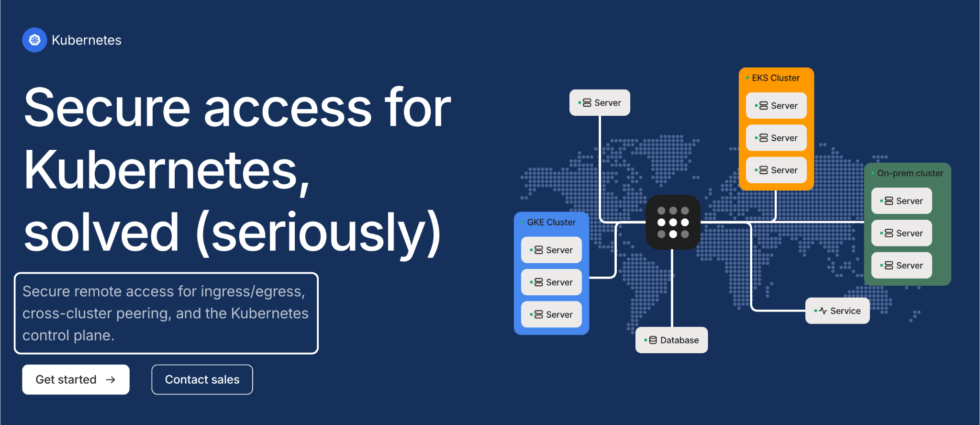
✓ ด่าน: The service shows up as its own device in the Machines list.
Step 3: Open It by Name
Hit the service DNS name from your phone or laptop.
✅ ผลลัพธ์: Internal dashboards stay off the public internet but remain accessible to your team.
💡 เคล็ดลับสำหรับมืออาชีพ: Use the operator’s API server proxy so kubectl works without a public control plane.
วิธีใช้งาน Tailscale Edge & IoT Deployments
การใช้งาน Edge และ IoT lets you manage a Raspberry Pi fleet or a shelf of sensors from one dashboard.
นี่คือวิธีการใช้งานทีละขั้นตอน
Step 1: Flash and Install
Install the client on each Raspberry Pi with the standard Linux command.
Step 2: Use Ephemeral Keys
Ephemeral auth keys clean up stale entries when a device goes offline for good.
นี่คือหน้าตาของมัน:
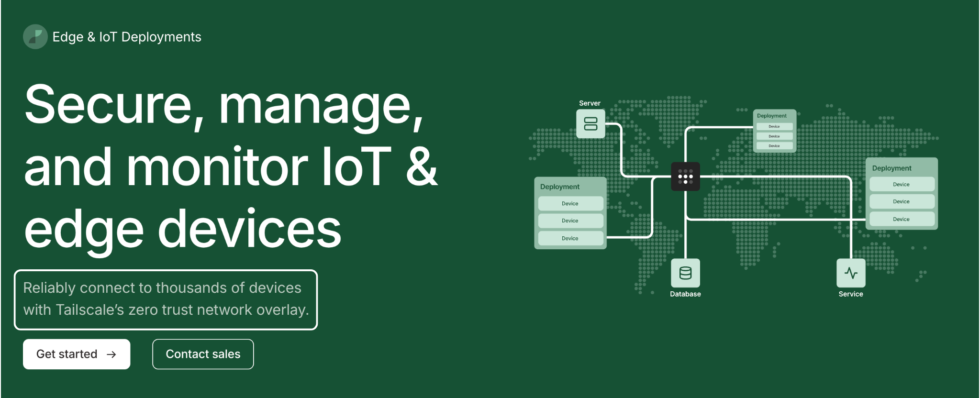
✓ ด่าน: Each board reports online and answers SSH over its tailnet name.
Step 3: Name Every Node
Rename each machine so the hostname tells you where it sits.
✅ ผลลัพธ์: Field hardware is reachable without static IPs, dynamic DNS or open ports.
💡 เคล็ดลับสำหรับมืออาชีพ: Set a device to never expire, or a remote sensor will drop off after 180 days and need a physical visit.
How to Use Tailscale Cloud connectivity
Cloud connectivity lets you let a cloud app read an on-premise database without a public route.
นี่คือวิธีการใช้งานทีละขั้นตอน
Step 1: Route the On-Prem Side
Run a subnet router next to the database and advertise its range.
Step 2: Join the Cloud Workload
Install the client inside the cloud VM or container.
นี่คือหน้าตาของมัน:
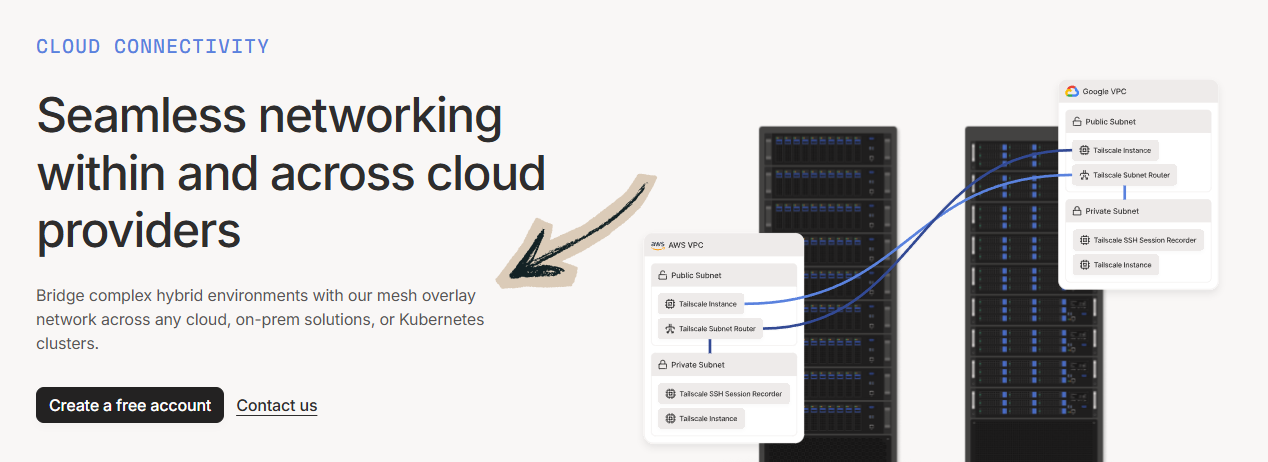
✓ ด่าน: The application connects to the private host by its internal IP.
Step 3: Lock It Down
Write an ACL that allows only that workload to reach the database port.
✅ ผลลัพธ์: Cloud and on-prem traffic stays encrypted end to end with no bastion host.
💡 เคล็ดลับสำหรับมืออาชีพ: Turn on MagicDNS so the connection string uses a stable name instead of a changing address.
How to Use Tailscale Secure AI
การรักษาความปลอดภัยของ AI lets you keep a GPU box or local model server private while your laptop still reaches it.
นี่คือวิธีการใช้งานทีละขั้นตอน
Step 1: Bind Locally
Run the model server on localhost or on the tailnet interface only.
Step 2: Add the GPU Host
Install the client on the GPU machine and confirm it is connected.
นี่คือหน้าตาของมัน:
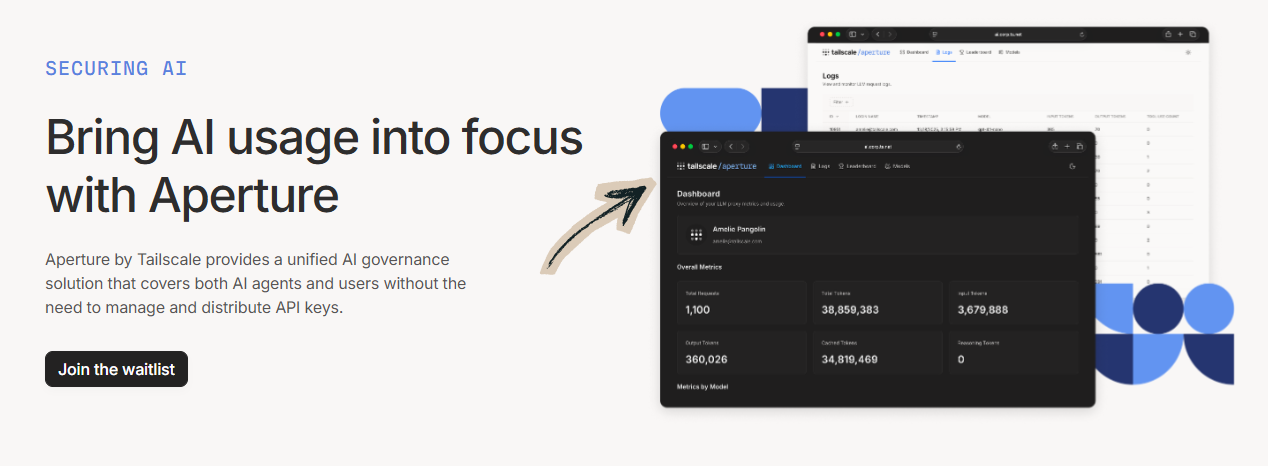
✓ ด่าน: The model answers requests from your laptop and nowhere else.
Step 3: Point Your Tools at It
Use the tailnet hostname as the API endpoint in your app.
✅ ผลลัพธ์: Your private model is usable from anywhere and invisible to the public internet.
💡 เคล็ดลับสำหรับมืออาชีพ: Share the node with one teammate instead of the whole tailnet when you need a second pair of eyes.
How to Use Tailscale Zero Trust networking
Zero Trust networking lets you grant access per user and per device instead of trusting everyone on the network.
นี่คือวิธีการใช้งานทีละขั้นตอน
Step 1: Open the Access Controls
Edit the policy file in the admin console.
Step 2: Write Narrow Rules
Allow each group to reach only the ports it needs.
นี่คือหน้าตาของมัน:
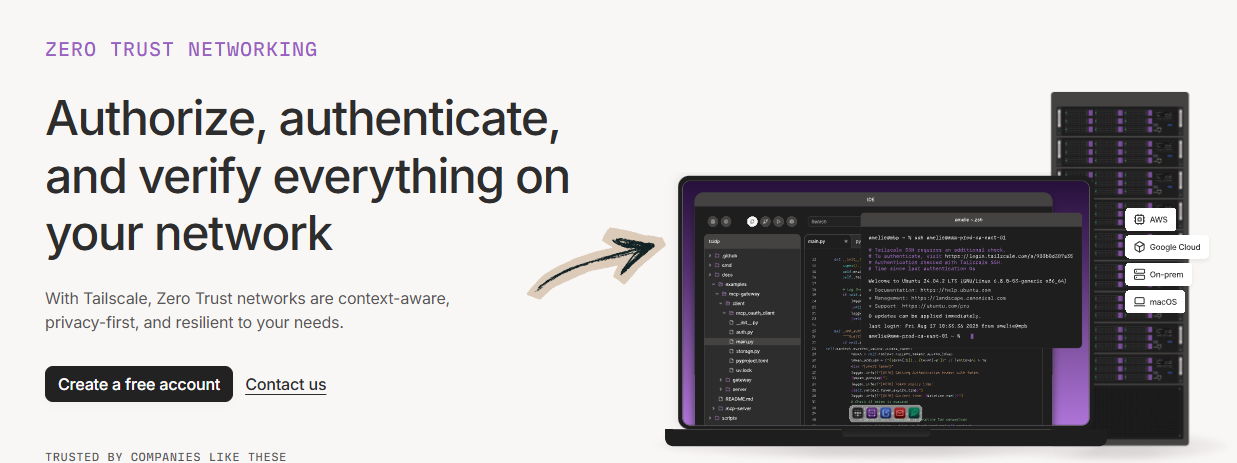
✓ ด่าน: A test account is blocked from a server it should not touch.
Step 3: Require Device Posture
Turn on device approval so new hardware waits for a human check.
✅ ผลลัพธ์: Access follows identity, so a stolen laptop does not hand over the whole network.
💡 เคล็ดลับสำหรับมืออาชีพ: Use the ACL preview tab before saving, since a bad rule can lock you out of your own machines.
เคล็ดลับและเทคนิคลัดจาก Tailscale Pro
If you are interested in getting more from your tailnet, start with these.
Handy Commands
| การกระทำ | สั่งการ |
|---|---|
| Check connections | สถานะเกล็ดหาง |
| Connect this machine | เกล็ดหางขึ้น |
| Send a file | tailscale file cp |
| Test a path | tailscale ping |
คุณสมบัติที่ซ่อนอยู่ซึ่งคนส่วนใหญ่มองข้ามไป
- Exit node: Route all internet traffic through one device. For example, a laptop in San Francisco can browse through your home connection. Exit nodes are chosen per client.
- Taildrop: Send files between your own devices without the cloud, straight from the share sheet on a phone.
- MagicDNS: Human-readable hostnames replace raw IP addresses, so
ssh piworks from any client. - Tailscale Serve: Publish a local web server to your tailnet over HTTPS with one command.
ข้อผิดพลาดทั่วไปที่ควรหลีกเลี่ยงในการระบายสีเกล็ดหาง
Mistake #1: Expecting it to hide your browsing by default
❌ ผิด: Installing the app and assuming websites now see a different IP address.
✅ ด้านขวา: Only tailnet traffic is routed by default. Pick an exit node if you want your public IP hidden too.
Mistake #2: Forgetting to approve subnet routes
❌ ผิด: Running the advertise command, then wondering why the home network is unreachable.
✅ ด้านขวา: Approve the route in the admin console and enable IP forwarding on the host.
Mistake #3: Ignoring key expiry
❌ ผิด: Leaving a headless server to expire after 180 days and losing remote access.
✅ ด้านขวา: Disable key expiry on servers you cannot physically reach.
การแก้ไขปัญหาเครื่องชั่งท้ายเรือ
Problem: Devices connect but the link feels slow
สาเหตุ: A direct peer connection failed, so traffic is going through a DERP relay server.
แก้ไข: วิ่ง ตาข่ายเกล็ดหาง, then open UDP 41641 outbound or turn off strict NAT on the router.
Problem: A machine shows as offline
สาเหตุ: The client stopped, or its node key expired.
แก้ไข: Restart the service, run เกล็ดหางขึ้น again and re-authenticate in the browser.
A machine configured months ago sometimes just needs connecting once more.
Problem: Hostnames do not resolve
สาเหตุ: MagicDNS is off, or another VPN client is holding the DNS settings.
แก้ไข: Enable MagicDNS in the admin console and disconnect the other VPN.
📌 บันทึก: If none of these help, the Tailscale documentation and support team are both quick to answer.
เกล็ดหางคืออะไร?
เกล็ดหาง is a VPN service that builds a private mesh network between your own machines.
Think of it as a network cable that follows your devices around the world.
It is based on the WireGuard protocol, and its architecture avoids the single point of failure a central VPN server creates.
Traffic takes the shortest path possible, usually a direct peer-to-peer hop, with encrypted packets end to end.
Here is the short version:
ประกอบด้วยคุณสมบัติหลักดังต่อไปนี้:
- VPN สำหรับธุรกิจ: One tailnet for the whole company, with single-sign-on and admin roles.
- การเข้าถึงระยะไกลที่ปลอดภัย: Reach a home server or office host without exposing services to the internet.
- การเชื่อมต่อเครือข่ายระหว่างไซต์: Subnet routers link entire networks through one gateway device.
- การเชื่อมต่อเครือข่ายมัลติคลาวด์: Servers across providers share one flat set of IP addresses.
- คูเบอร์เน็ตส์: Cluster services become tailnet devices instead of public endpoints.
- การใช้งาน Edge และ IoT: A Raspberry Pi in the field stays accessible with no open ports.
- การเชื่อมต่อระบบคลาวด์: Cloud workloads reach on-prem hosts over an encrypted path.
- การรักษาความปลอดภัยของ AI: Local model servers stay private while your tools still connect.
- Zero Trust networking: Access rules follow the user and the device, not the network.
For the full breakdown, see our รีวิว Tailscale.
การกำหนดราคาสินค้าคงเหลือท้ายเรือ
Here is what Tailscale costs in 2026:
| วางแผน | ราคา | เหมาะสำหรับ |
|---|---|---|
| ส่วนตัว | ฟรีตลอดไป $0 | One user, home network and side projects |
| ส่วนบุคคลพลัส | 5 ดอลลาร์/เดือน | Enthusiasts who want more devices and a few users |
ทดลองใช้งานฟรี: The Personal plan is free forever, so there is nothing to trial.
รับประกันคืนเงิน: Paid plans are monthly, so you cancel rather than claim a refund.
The Personal plan is free for personal use and covers 20 devices on a single tailnet.
Team plans add advanced SSO, unlimited access control, admin roles and enterprise support.
Here is the pricing page as it stands:
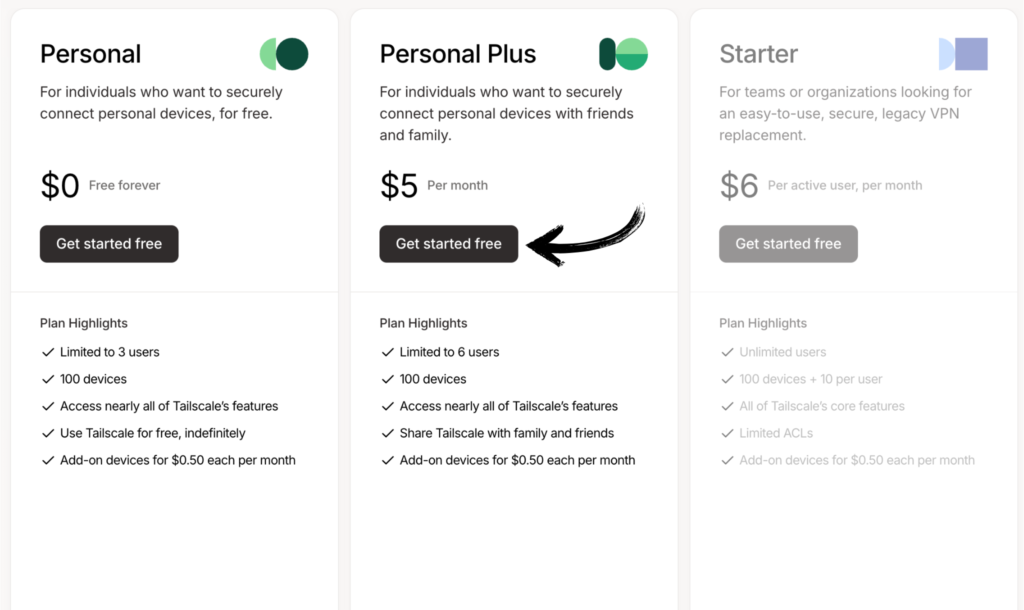
💰 คุ้มค่าที่สุด: Personal — free forever, and enough for a home lab with a Raspberry Pi, a NAS and a laptop.
เกล็ดหางเทียบกับทางเลือกอื่นๆ
Most tools on this list are privacy VPNs. Tailscale is a networking tool, so compare on the job you need done.
| เครื่องมือ | เหมาะสำหรับ | ราคา | การให้คะแนน |
|---|---|---|---|
| เกล็ดหาง | Private device networks | 0 ดอลลาร์/เดือน | ⭐ 4.6 |
| NordVPN | การสตรีมมิ่งและความเป็นส่วนตัว | 12.99 ดอลลาร์/เดือน | ⭐ 4.7 |
| ExpressVPN | Speed and ease | 12.95 ดอลลาร์/เดือน | ⭐ 4.6 |
| โปรตันVPN | Privacy and free tier | 9.99 ดอลลาร์สหรัฐฯ ต่อเดือน | ⭐ 4.5 |
| เซิร์ฟชาร์ค VPN | อุปกรณ์ไม่จำกัดจำนวน | 12.95 ดอลลาร์/เดือน | ⭐ 4.5 |
| ไซเบอร์โกสต์ | เซิร์ฟเวอร์สตรีมมิ่ง | 12.99 ดอลลาร์/เดือน | ⭐ 4.3 |
| การเข้าถึงอินเทอร์เน็ตส่วนตัว | Configurable client | $11.95/mo | ⭐ 4.4 |
| PureVPN | Budget plans | $10.95/mo | ⭐ 4.2 |
ตัวเลือกที่น่าสนใจ:
- ดีที่สุดโดยรวม: Tailscale — nothing else connects your own machines this quickly.
- งบประมาณที่ดีที่สุด: Tailscale — the free plan covers most home setups.
- เหมาะสำหรับผู้เริ่มต้น: ExpressVPN — one button, no networking knowledge needed.
- Best for hiding traffic: ProtonVPN — audited clients and a genuine free tier.
🎯 ทางเลือกอื่นๆ สำหรับเกล็ดหาง
Looking for Tailscale alternatives? Here are the options worth a look:
- 🚀 NordVPN: Huge server network for streaming and privacy, though it hides your traffic rather than linking your own devices.
- ⭐ ExpressVPN: Fast consumer VPN with apps on nearly every platform, built for location switching instead of private device networking.
- 💰 POWN บริสุทธิ์: Budget subscription VPN with a dedicated IP add-on, useful if you only need a hidden public address.
- 💼 Surfshark VPN: Unlimited device connections on one account, a good pick for families who want traffic encryption everywhere.
- 🔒 ProtonVPN: Privacy-first provider with a solid free tier and open-source clients audited by outside firms.
- 👶 ProvadoVPN: สืบค้นเมื่อ ค.ศ Simple free tier with a small monthly ข้อมูล allowance, aimed at people new to VPN apps.
- 🎯 Ad Card VOPN: Pairs traffic encryption with ad blocking, handy on a phone where trackers are the main annoyance.
- 🏢 เวอร์ชวลชีลด์: Consumer privacy bundle with identity monitoring, sold mainly to households rather than technical users.
- 🔧 StrongVPN: Long-running provider with router support, a fit if you want one device covering the whole home network.
- 📊 ออร่าVPN: Part of a wider identity protection suite, bundling a VPN with credit and dark web monitoring.
- 🔥 ไซเบอร์Ghost: Streaming-tuned servers and a very long refund window, built for media rather than infrastructure.
- 🧠 McAfe VPNN: Bundled with McAfee antivirus, convenient if you already pay for the ความปลอดภัย ห้องสวีท
- ⚡ อินเตอร์เน็ตส่วนตัว การเข้าถึง: Configurable client with per-app rules and a no-logs record tested in court.
- 🌟 มิสเตอรียม: Decentralised node marketplace where users pay for bandwidth from other people’s hardware.
- 🎨 SafeShell VPN: Focused on streaming access with region-specific modes for major platforms.
- 🚀 Oyster VPN: Small provider with cheap long-term plans and a straightforward app on phone and desktop.
ดูรายชื่อทั้งหมดได้ที่หน้าของเรา ทางเลือกสำหรับเกล็ดหาง แนะนำ.
⚔️ เปรียบเทียบเกล็ดหาง
Here is the head-to-head against each one:
- Tailscale เทียบกับ NordVPN: NordVPN wins for anonymous browsing. Tailscale wins when you want to reach your own machines.
- Tailscale เทียบกับ ExpressVPN: ExpressVPN is simpler for casual users. Tailscale gives you a real private network.
- Tailscale เทียบกับ PureVPN: PureVPN is cheaper for streaming. Tailscale is free for personal use and far better for remote access.
- Tailscale เทียบกับ Surfshark VPN: Surfshark covers more devices per plan. Tailscale connects those devices to each other.
- Tailscale เทียบกับ ProtonVPN: ProtonVPN is stronger on anonymity. Tailscale is stronger on connectivity between your own servers.
- Tailscale เทียบกับ PrivadoVPN: PrivadoVPN suits light browsing. Tailscale suits anyone running a home server.
- Tailscale เทียบกับ AdGuard VPN: AdGuard blocks ads better. Tailscale handles private networks that AdGuard never touches.
- Tailscale vs VirtualShield: VirtualShield targets families. Tailscale targets developers and IT teams.
- Tailscale เทียบกับ StrongVPN: StrongVPN is easier on an old router. Tailscale gives per-device access rules.
- Tailscale เทียบกับ AuraVPN: Aura bundles more privacy tools. Tailscale does one job properly.
- เทลสเกล ปะทะ ไซเบอร์โกสต์: CyberGhost unblocks more catalogues. Tailscale reaches your NAS and Raspberry Pi.
- Tailscale เทียบกับ McAfee VPN: McAfee is convenient if bundled. Tailscale is the better standalone network tool.
- Tailscale เทียบกับ การเข้าถึงอินเทอร์เน็ตส่วนตัว: PIA offers deeper tuning for privacy. Tailscale offers direct peer-to-peer links.
- เทลสเกล ปะทะ มิสเทอเรียม: Mysterium is more experimental. Tailscale is production-ready for daily work.
- Tailscale เทียบกับ SafeShell VPN: SafeShell is aimed at viewers. Tailscale is aimed at ผู้สร้าง.
- Tailscale เทียบกับ Oyster VPN: Oyster costs less monthly. Tailscale costs nothing for a personal tailnet.
เริ่มใช้งาน Tailscale ได้เลยตอนนี้
You now know how to use Tailscale across every major feature:
- ✅ VPN สำหรับธุรกิจ
- ✅ การเข้าถึงระยะไกลที่ปลอดภัย
- ✅ การเชื่อมต่อเครือข่ายระหว่างไซต์
- ✅ การเชื่อมต่อเครือข่ายมัลติคลาวด์
- ✅ คูเบอร์เน็ตส์
- ✅ การใช้งาน Edge และ IoT
- ✅ Cloud connectivity
- ✅ การรักษาความปลอดภัยของ AI
- ✅ Zero Trust networking
ขั้นตอนต่อไป: Install the client on two devices and run สถานะเกล็ดหาง.
คนส่วนใหญ่มักเริ่มต้นด้วยการตั้งค่าการเข้าถึงระยะไกลที่ปลอดภัย (Secure Remote Access)
ใช้เวลาน้อยกว่าห้านาที
ถาม บ่อย ๆ
วิธีใช้งาน Tailscale อย่างถูกต้องมีดังนี้
Create a free account, install the client on two or more devices, and log in with the same account. Each machine gets a 100.x.x.x IP address and connects by name.
โปรแกรม Tailscale สามารถใช้งานได้ฟรีสำหรับการใช้งานส่วนตัวหรือไม่?
Yes. The Personal plan is free forever and covers 20 devices on one tailnet. Personal Plus costs $5/per month if you want more devices and a few extra users.
ฉันควรเปิดใช้งาน Tailscale ไว้ตลอดเวลาหรือไม่?
Yes, for most people. It only routes tailnet traffic by default, so it barely touches battery or speed unless you turn on an exit node.
Tailscale ซ่อนที่อยู่ IP ของฉันหรือไม่?
Not by default, because normal browsing skips the tailnet. Enable an exit node and your public traffic leaves through that device instead of your own connection.
Tailscale สามารถมองเห็นปริมาณการรับส่งข้อมูลของฉันได้หรือไม่?
No. Packets are encrypted between devices with WireGuard keys. The coordination server handles public key exchange and device lists, never the contents of your connections.
 English
 Spanish
 Chinese
 German
 French
 Arabic
 Russian
 Portuguese
 Japanese
 Korean
 Italian
 Turkish
 Dutch
 Polish
 Indonesian
 Thai
 Vietnamese