เริ่มต้นใช้งานอย่างรวดเร็ว
คู่มือนี้ครอบคลุมทุกคุณสมบัติของ OpenVPN:
- เริ่มต้นใช้งาน — Install openvpn software and make your first vpn connection
- วิธีใช้งานการเข้าถึงระยะไกลที่ปลอดภัย — Lets remote staff reach private servers through one encrypted vpn tunnel.
- วิธีใช้งานการสื่อสาร IoT ที่ปลอดภัย — Keeps cameras, sensors and controllers off the open internet.
- สร้างการเข้าถึงที่ปลอดภัยสำหรับแอปพลิเคชัน SaaS — Sends SaaS traffic through one fixed address your vendors can allowlist.
- วิธีใช้งานเครือข่ายระหว่างไซต์ — Joins two offices into one network without paying for leased lines.
- How to Use Enforce Zero Trust Access — Limits each group to the exact systems it needs, nothing more.
- How to Use DNS Security and Content Filtering — Blocks malicious and unwanted domains before anyone loads them.
- วิธีใช้งานการป้องกัน SaaS — Shows who touches which cloud app, and blocks the rest.
ระยะเวลาที่ใช้: แต่ละฟีเจอร์ใช้เวลา 5 นาที
นอกจากนี้ในคู่มือนี้ยังมี: เคล็ดลับสำหรับมืออาชีพ | ข้อผิดพลาดที่พบบ่อย | การแก้ไขปัญหา | ความละเอียด | ตัวเลือกต่าง ๆ
เหตุใดจึงควรเชื่อถือคู่มือนี้
I’ve run OpenVPN for three years across laptops, routers and a rented Linux box. Every step here comes from my own openvpn installation, not vendor screenshots.
OpenVPN is the openvpn protocol most paid VPN apps quietly run underneath.
You can use it two ways.
Import an ovpn file from a ยูวี provider, or run your own vpn server.
This guide walks through both, step by step.
คู่มือการใช้งาน OpenVPN
This How to Use OpenVPN tutorial covers install, configuration files, certificates and daily use.
OpenVPN
Run your own encrypted ยูวี tunnel on hardware you control. OpenVPN Access Server is free for three simultaneous client connections, with no card needed to start.
เริ่มต้นใช้งาน OpenVPN
ก่อนใช้งานฟีเจอร์ใดๆ โปรดทำการตั้งค่าครั้งแรกนี้ให้เสร็จสิ้นก่อน
It takes about ten minutes on a fresh machine.
Step 1: Install OpenVPN
Download the openvpn package for your system from the official site.
On Windows the installer drops files into Program Files and adds the OpenVPN GUI.
Most linux distributions install openvpn with a single apt or dnf command.
✓ ด่าน: Running openvpn –version confirms you have installed openvpn correctly.
Step 2: Get Your Configuration File
Every vpn service hands you an ovpn file, or you build your own.
Most providers ship several ovpn configuration files, one per city.
Self-hosting? Copy the sample server configuration file from the docs folder.
That sample server template already carries sane defaults for a routed vpn.
On Linux, everything lives under /etc/openvpn once you configure openvpn.
That folder holds the server.conf file, your certificate files and keys.
Creating configuration files by hand works, but the sample saves an hour.
Here’s what the working folder looks like:
✓ ด่าน: Your config files sit together in one folder you can find again.
ขั้นตอนที่ 3: เชื่อมต่อเป็นครั้งแรก
Import the profile into OpenVPN Connect, or place it in the client folder.
On Windows, right-click the openvpn gui and run it as administrator.
Then pick the profile and click Connect.
Watch the log window as it scrolls past.
Older guides mention a now authenticated certificate header line.
That only means your openvpn configuration file passed its checks.
✅ เสร็จเรียบร้อยแล้ว: The log ends with initialization sequence completed. You’re connected.
How to Use OpenVPN Secure Remote Access Tool
การเข้าถึงระยะไกลที่ปลอดภัย lets you give staff an encrypted vpn tunnel into private servers from any location.
นี่คือวิธีการใช้งานทีละขั้นตอน
Step 1: Add Your Users
Open the Access Server admin panel in your browser.
Add each teammate under User Management and set a password.
Step 2: Send Out the Profile
Click the user, then download their client configuration file.
Share that .ovpn file over a private channel, never email.
Keep all client configuration files in one folder for easy revocation.
นี่คือหน้าตาของมัน:
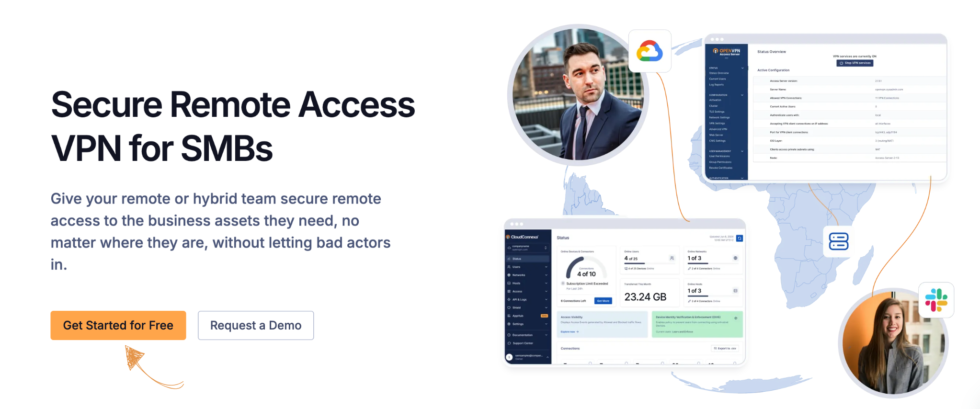
✓ ด่าน: The profile downloads as a single .ovpn file with keys inside.
ขั้นตอนที่ 3: เชื่อมต่อและยืนยัน
Import the profile into OpenVPN Connect and hit connect.
Check your public ip address on iplocation.net to confirm the swap.
✅ ผลลัพธ์: Your team now reaches internal apps over an encrypted openvpn connection.
💡 เคล็ดลับสำหรับมืออาชีพ: Name each client configuration file after the person, not the device. Revoking access later takes seconds.
How to Use OpenVPN Secure IoT Communicator
การสื่อสาร IoT ที่ปลอดภัย lets you put cameras, sensors and controllers on a private encrypted link.
นี่คือวิธีการใช้งานทีละขั้นตอน
Step 1: Create a Device Group
Make a separate group for hardware, apart from human users.
Give it read-only access to the subnet it needs.
Step 2: Pin Static Addresses
Use client specific rules to hand each device a fixed address.
Fixed ip addresses make firewall logs readable months later.
นี่คือหน้าตาของมัน:
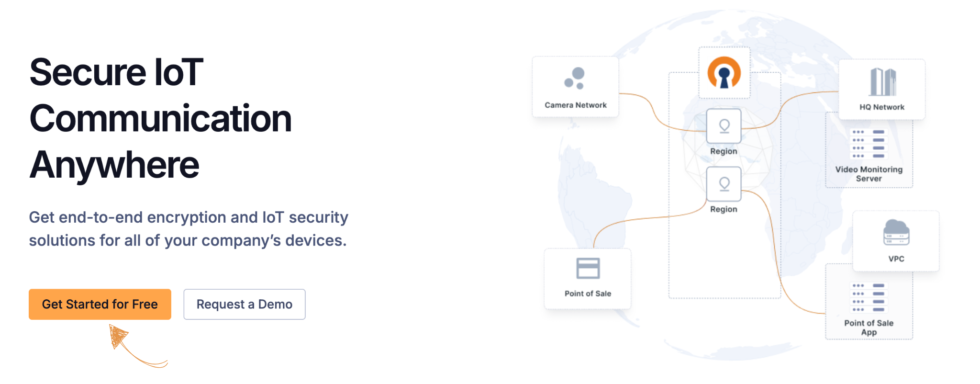
✓ ด่าน: Each device shows the same address on every reconnect.
Step 3: Load the Profile on Device
Copy the ovpn file to the device and start the openvpn service.
Set it to reconnect on boot so nothing drops silently.
✅ ผลลัพธ์: Your hardware talks home over a private tunnel instead of open ports.
💡 เคล็ดลับสำหรับมืออาชีพ: Give IoT อุปกรณ์ their own client keys. One compromised sensor should never expose the rest.
How to Create OpenVPN Secure Access to SaaS Applications
สร้างการเข้าถึงที่ปลอดภัยสำหรับแอปพลิเคชัน SaaS lets you route SaaS traffic through one fixed public ip address you can allowlist.
นี่คือวิธีการใช้งานทีละขั้นตอน
Step 1: Note Your Gateway Address
Find the public ip address of your vpn server machine.
That single address becomes your front door to every SaaS vendor.
Step 2: Allowlist It With Vendors
Paste the address into each SaaS admin panel under IP restrictions.
Most tools call this trusted IP ranges or network allowlisting.
นี่คือหน้าตาของมัน:
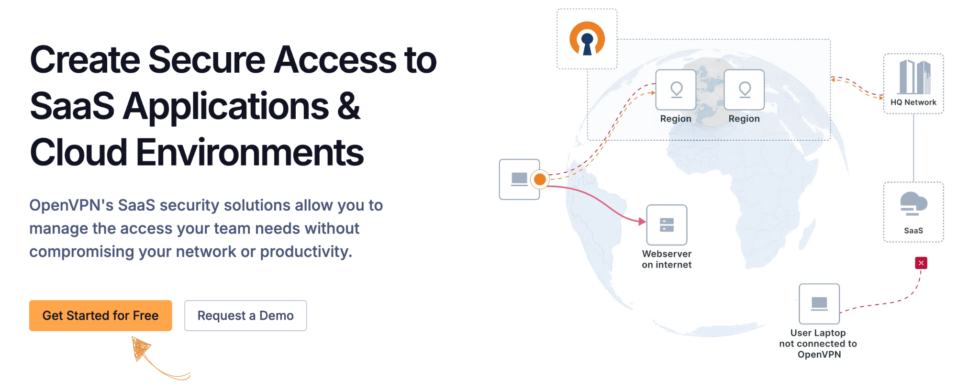
✓ ด่าน: Logging in from outside the tunnel now gets refused.
Step 3: Force Traffic Through the Tunnel
Turn on redirect gateway so all traffic uses the vpn connection.
Split tunnelling here would break the allowlist you just built.
✅ ผลลัพธ์: Stolen passwords stop working unless the attacker is inside your vpn.
💡 เคล็ดลับสำหรับมืออาชีพ: Keep a second gateway address on standby. If your host rotates addresses, logins break ทันที.
วิธีใช้งาน OpenVPN Site-to-Site Networking
การเชื่อมต่อเครือข่ายระหว่างไซต์ lets you join two offices into one private network without leased lines.
นี่คือวิธีการใช้งานทีละขั้นตอน
Step 1: Pick Non-Overlapping Subnets
Each site needs its own range, such as 10.8.1.0 and 10.8.2.0.
Matching ranges are the number one cause of routing failures.
Step 2: Set the Gateway Role
Mark one site as gateway inside the openvpn server configuration.
This runs a routed vpn, which suits office links better than bridging.
นี่คือหน้าตาของมัน:
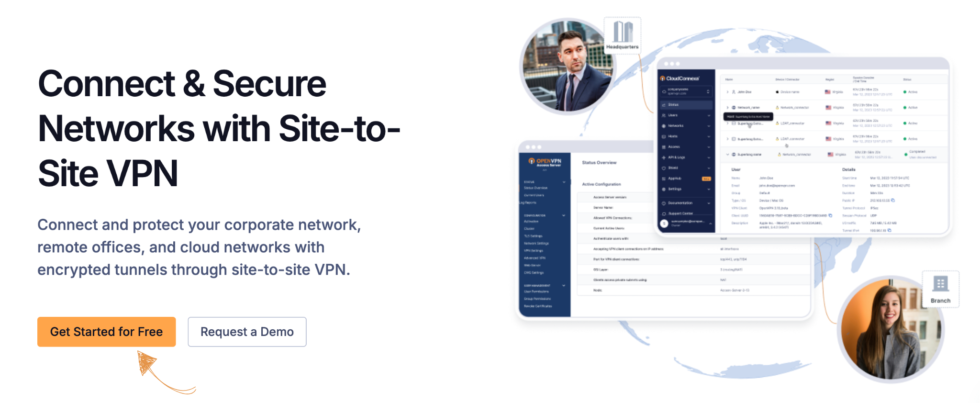
✓ ด่าน: A ping from one office reaches a printer at the other.
Step 3: Push the Routes
Add push route lines so each side learns the other subnet.
Restart openvpn on both ends to apply the change.
✅ ผลลัพธ์: Both offices share files and printers as if they sat in one building.
💡 เคล็ดลับสำหรับมืออาชีพ: Document the subnet map before you build. Future you will thank present you during outages.
How to Use OpenVPN Enforce Zero Trust Access
บังคับใช้การเข้าถึงแบบ Zero Trust lets you limit every user group to the exact systems it needs.
นี่คือวิธีการใช้งานทีละขั้นตอน
Step 1: Map Groups to Systems
List which teams truly need billing, staging or production access.
Most people need far less than they currently hold.
Step 2: Write the Access Rules
Set per-group subnet rules in the admin panel or the server config file.
Deny everything first, then open only what the group requires.
นี่คือหน้าตาของมัน:
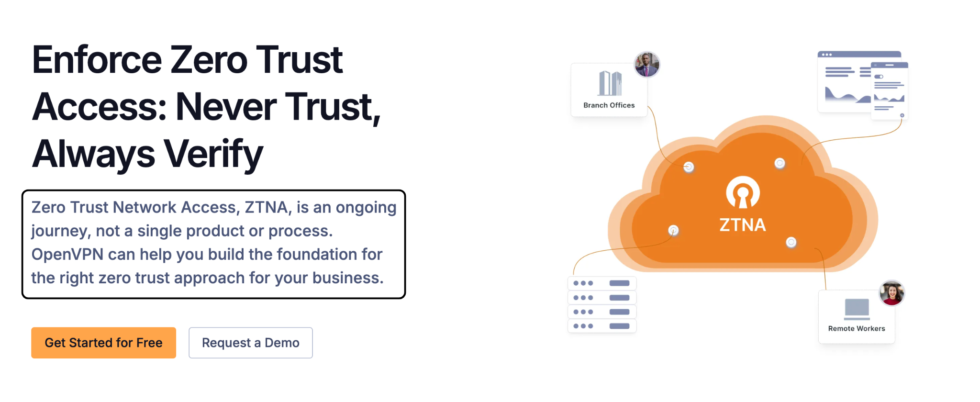
✓ ด่าน: A test account can reach its own subnet and nothing else.
Step 3: Add a Second Factor
Turn on multi-factor authentication alongside your server and client certificates.
Certificates prove the machine, MFA proves the person.
✅ ผลลัพธ์: One stolen laptop no longer opens your whole network.
💡 เคล็ดลับสำหรับมืออาชีพ: Review group rules every quarter. Access creep happens quietly as people change roles.
How to Use OpenVPN DNS Security and Content Filtering
DNS ความปลอดภัย and Content Filtering lets you block malicious domains before anyone on the tunnel loads them.
นี่คือวิธีการใช้งานทีละขั้นตอน
Step 1: Push Your Resolvers
Add push dhcp-option DNS lines to send dns servers to clients.
Without this, laptops leak lookups to whatever café router they meet.
Step 2: Choose Filter Categories
Switch on categories such as malware, phishing and adult content.
Start narrow, then widen once support tickets stay quiet.
นี่คือหน้าตาของมัน:
✓ ด่าน: Your resolver appears in the client log, not the local router.
Step 3: Test a Blocked Domain
Visit a known test domain from a connected client machine.
A block page confirms filtering runs inside the tunnel.
✅ ผลลัพธ์: Every connected device inherits the same filtering, even on โรงแรม Wi-Fi
💡 เคล็ดลับสำหรับมืออาชีพ: Whitelist your own domains first. Filters love to block internal tools on day one.
How to Use OpenVPN SaaS Protector
การป้องกัน SaaS lets you watch and lock down how your team signs into cloud apps.
นี่คือวิธีการใช้งานทีละขั้นตอน
Step 1: Turn On Access Logging
Enable connection logging for client connections in the admin panel.
You want names, times and addresses, not just totals.
Step 2: Review Weekly Patterns
Scan for logins at odd hours or from unexpected countries.
Odd patterns show up long before a breach does.
นี่คือหน้าตาของมัน:
✓ ด่าน: The log shows each session with a user name attached.
Step 3: Cut Off Stale Accounts
Revoke the client certificate the day someone leaves.
Revocation beats password changes because the key file dies too.
✅ ผลลัพธ์: You can answer who accessed what, and when, in under a minute.
💡 เคล็ดลับสำหรับมืออาชีพ: Export logs monthly to cold storage. Auditors ask for history your dashboard no longer keeps.
เคล็ดลับและทางลัดสำหรับ OpenVPN Pro
After three years of configuring openvpn, these are the habits that stuck.
This is the terminal view I keep open while testing:

Commands Worth Memorising
| การกระทำ | ทางลัด |
|---|---|
| Connect from terminal | sudo openvpn –config client.ovpn |
| Restart openvpn service | sudo systemctl restart openvpn@server |
| Watch the live log | sudo journalctl -fu openvpn@server |
| Check the tunnel interface | ip addr show tun0 |
คุณสมบัติที่ซ่อนอยู่ซึ่งคนส่วนใหญ่มองข้ามไป
- Client specific rules: Drop a file named after the client into the ccd folder. Configuring client specific rules lets you pin routes per user.
- ส่วนติดต่อการจัดการ: Add a management line to the server config file, then telnet in to watch client connect events live.
- The vars file: Edit vars inside the easy-rsa directory once, and every certificate signing request inherits your details automatically.
- Offline signing: Keep the ca private key on an air-gapped machine, or a dedicated key server. Your server key then never travels.
ข้อผิดพลาดทั่วไปที่ควรหลีกเลี่ยงในการใช้งาน OpenVPN
Mistake #1: Emailing the Private Key
❌ ผิด: Sending certificate files and the private key as an email attachment.
✅ ด้านขวา: Hand over key files through a ตัวจัดการรหัสผ่าน or an encrypted share.
Mistake #2: Copying a Config Without Reading It
❌ ผิด: Pasting a random openvpn server configuration file from a forum thread.
✅ ด้านขวา: Start from the official sample configuration files, then change one line at a time.
Mistake #3: Forgetting IP Forwarding
❌ ผิด: Building the tunnel, then wondering why no website loads through it.
✅ ด้านขวา: Turn on ip forwarding and add the firewall rule before you blame the openvpn configuration.
การแก้ไขปัญหา OpenVPN
ปัญหา: การเชื่อมต่อ TLS ล้มเหลว
สาเหตุ: The client cannot reach the vpn server, or tls authentication keys do not match.
แก้ไข: Confirm port 1194 UDP is open, then check both ends share the same tls-crypt key.
Problem: Connected but No Internet
สาเหตุ: Traffic enters the tunnel and stops, usually missing routing or dns servers.
แก้ไข: Enable ip forwarding, add a NAT rule, and push a resolver to clients.
Problem: Certificate Verify Failed
สาเหตุ: The server certificate expired, or the ca server signed with a different root.
แก้ไข: Reissue the client certificate from the same CA, then restart openvpn on both sides.
📌 บันทึก: หากวิธีเหล่านี้ไม่สามารถแก้ไขปัญหาของคุณได้ โปรดติดต่อฝ่ายสนับสนุนของ OpenVPN
OpenVPN คืออะไร?
OpenVPN is open-source vpn software that builds an encrypted tunnel using SSL/TLS.
Think of it as a private hallway between two buildings on a public street.
The same openvpn software runs as both vpn server and vpn client.
ชมภาพรวมโดยย่อนี้:
ประกอบด้วยคุณสมบัติหลักดังต่อไปนี้:
- การเข้าถึงระยะไกลที่ปลอดภัย: Lets remote staff reach private servers through one encrypted vpn tunnel.
- การสื่อสาร IoT ที่ปลอดภัย: Keeps cameras, sensors and controllers off the open internet.
- Create Secure Access to SaaS Applications: Sends SaaS traffic through one fixed address your vendors can allowlist.
- การเชื่อมต่อเครือข่ายระหว่างไซต์: Joins two offices into one network without paying for leased lines.
- Enforce Zero Trust Access: Limits each group to the exact systems it needs, nothing more.
- DNS Security and Content Filtering: Blocks malicious and unwanted domains before anyone loads them.
- การปกป้อง SaaS: Shows who touches which cloud app, and blocks the rest.
It relies on a public key infrastructure, so both sides check each other before trusting anything.
That means server and client certificates, signed by one authority you control.
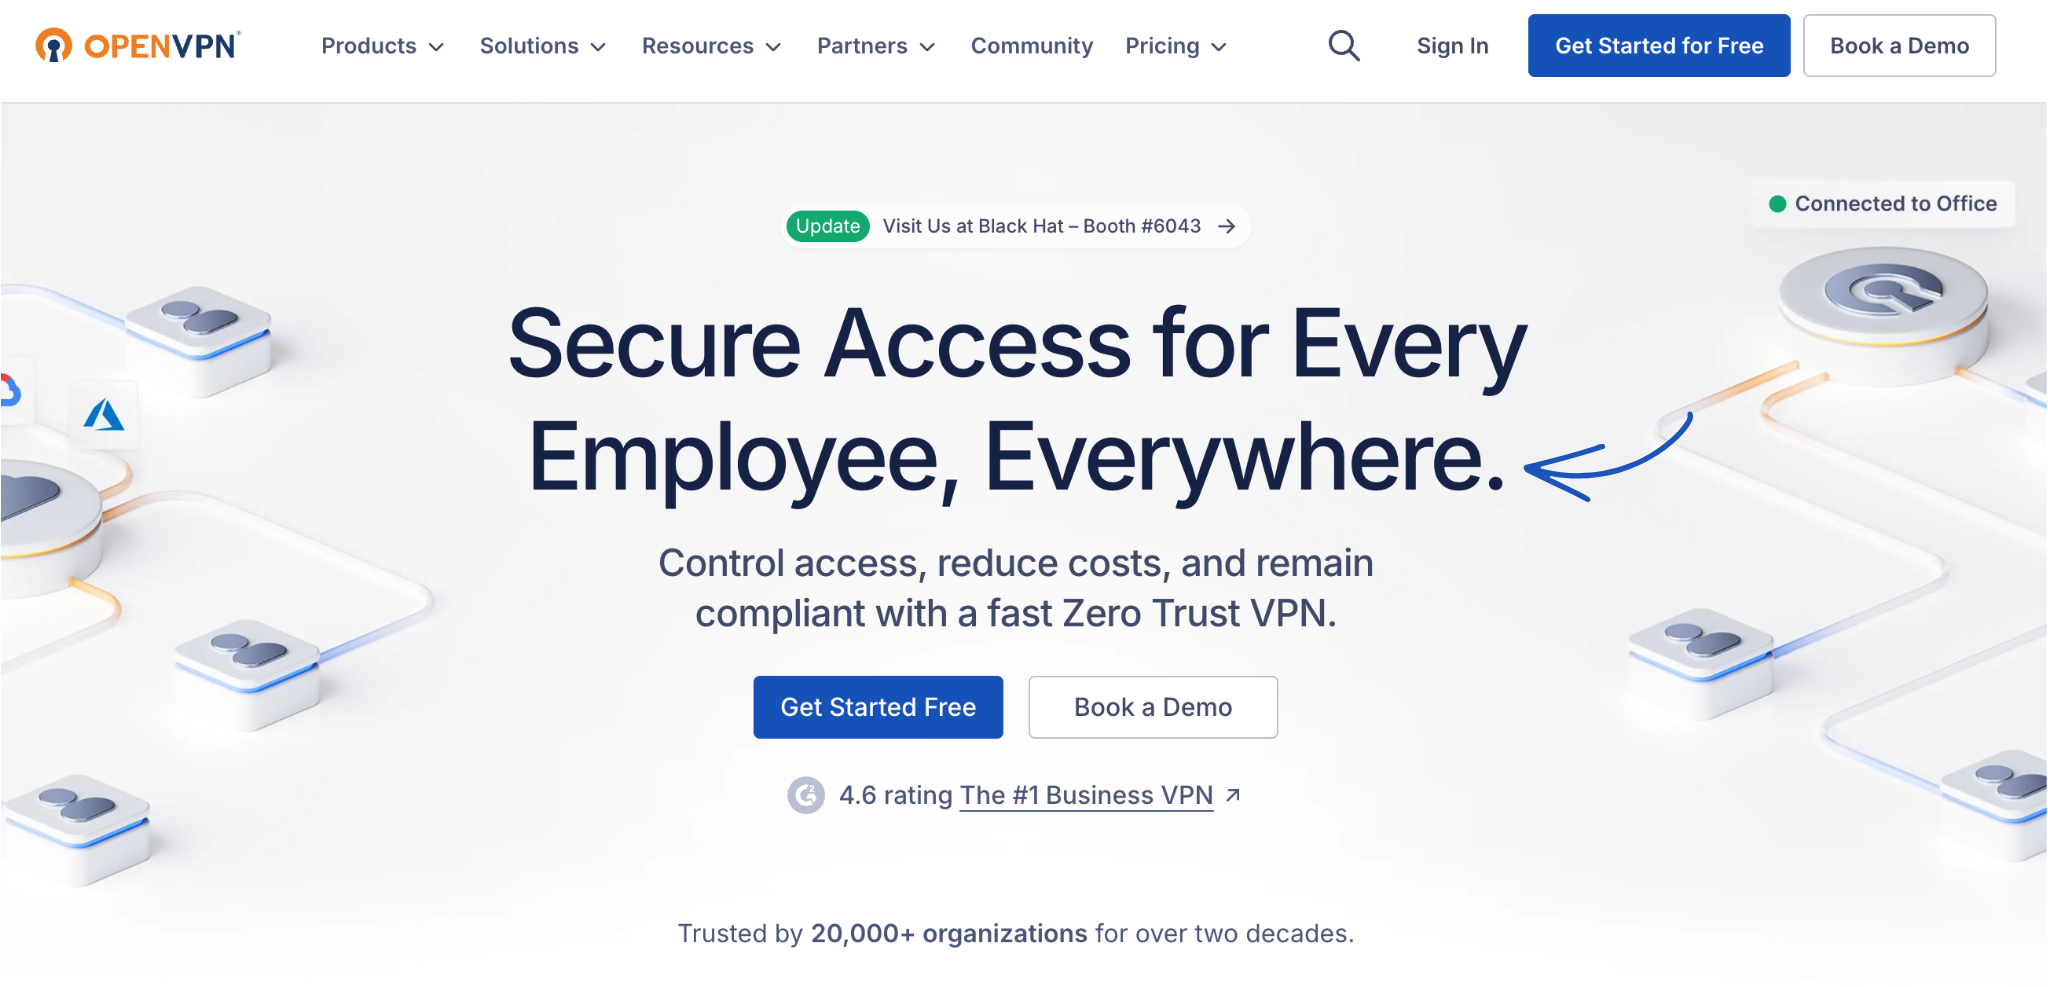
สำหรับรีวิวฉบับเต็ม โปรดดูที่หน้าของเรา รีวิว OpenVPN.
ราคา OpenVPN
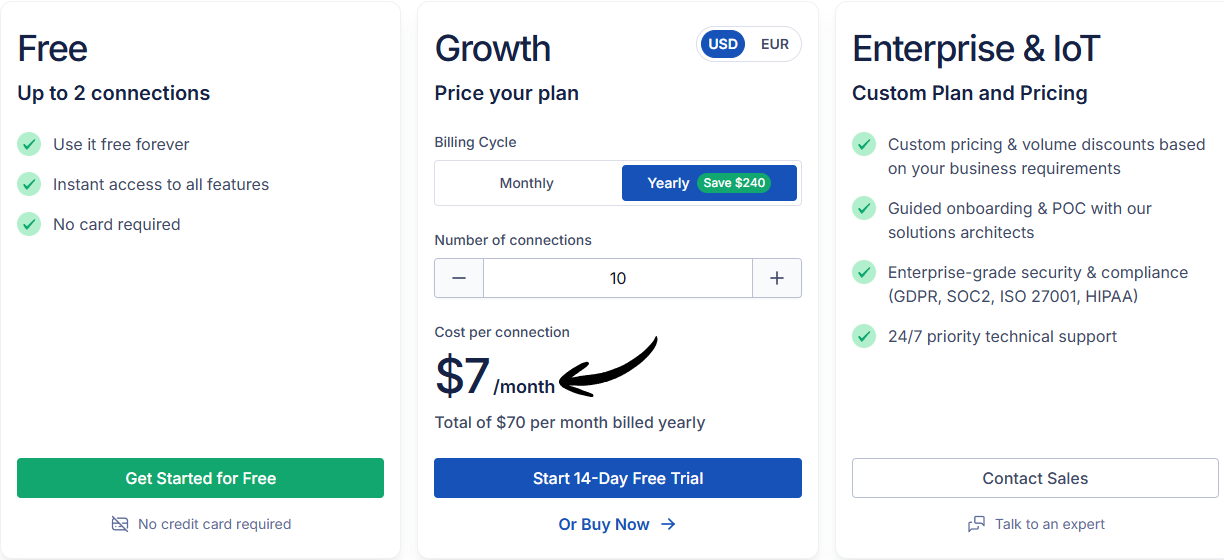
นี่คือราคาของ OpenVPN ในปี 2026:
| วางแผน | ราคา | เหมาะสำหรับ |
|---|---|---|
| ฟรี | $0 | Home labs and up to three connections |
| การเจริญเติบโต | 7 ดอลลาร์/เดือน | Small teams that need more seats |
| องค์กร | กำหนดเอง | Large fleets and compliance needs |
ทดลองใช้งานฟรี: Yes — the community edition stays free forever on your own hardware.
รับประกันคืนเงิน: Not needed on Free; paid plans bill per connection each month.
💰 คุ้มค่าที่สุด: Free — a $5 cloud box plus the openvpn package covers most households.
OpenVPN เทียบกับทางเลือกอื่นๆ
How does OpenVPN compare? Here is the landscape:
| เครื่องมือ | เหมาะสำหรับ | ราคา | การให้คะแนน |
|---|---|---|---|
| OpenVPN | Self-hosted control | 7 ดอลลาร์/เดือน | ⭐ 4.6 |
| NordVPN | Speed and server count | 30 ดอลลาร์สหรัฐฯ ต่อเดือน | ⭐ 4.8 |
| ExpressVPN | Simple apps everywhere | 4.99 ดอลลาร์/เดือน | ⭐ 4.7 |
| PureVPN | Budget long-term plans | $2.11/mo | ⭐ 4.3 |
| SurfsharkVPN | อุปกรณ์ไม่จำกัดจำนวน | 2.19 ดอลลาร์/เดือน | ⭐ 4.6 |
| โปรตันVPN | Privacy and free tier | 4.49 ดอลลาร์/เดือน | ⭐ 4.7 |
| ไพรวาโดVPN | ค่าเข้าชมที่ถูกที่สุด | 1.11 ดอลลาร์/เดือน | ⭐ 4.1 |
| ไซเบอร์โกสต์ | เซิร์ฟเวอร์สตรีมมิ่ง | 2.19 ดอลลาร์/เดือน | ⭐ 4.4 |
ตัวเลือกที่น่าสนใจ:
- ดีที่สุดโดยรวม: OpenVPN — you own the vpn server machine and every key.
- งบประมาณที่ดีที่สุด: PrivadoVPN — cheapest way to skip running your own server.
- เหมาะสำหรับผู้เริ่มต้น: ExpressVPN — one button, no configuration file to touch.
- เหมาะสำหรับผู้ที่ต้องการความเป็นส่วนตัวมากที่สุด: ProtonVPN — audited apps and a usable free plan.
🎯 ทางเลือกอื่นสำหรับ OpenVPN
กำลังมองหาทางเลือกอื่นแทน OpenVPN อยู่ใช่ไหม? นี่คือตัวเลือกที่ดีที่สุด:
- 🚀 Nordvpn: Huge server network and NordLynx speeds, though you never touch the underlying config file.
- 🌟 ExpressVPN: The most forgiving apps on every platform, with its own Lightway protocol instead of openvpn.
- 💰 POWN บริสุทธิ์: Long multi-year deals at low monthly cost, plus optional dedicated ip addresses.
- ⚡ Serverfshark VPN: เหตุการณ์ที่เกิดขึ้นใน ค.ศ Unlimited simultaneous devices on one account, which suits families and multiple clients.
- 🔒 ProtonVPN: Swiss privacy law, open-source apps and a free tier with no ข้อมูล cap.
- 👶 ProvadoVPN: สืบค้นเมื่อ ค.ศ Very cheap entry pricing and a simple interface for first-time vpn client users.
- 🎯 ไซเบอร์Ghost: Servers labelled by streaming service, so you skip the guesswork entirely.
ดูรายชื่อทั้งหมดได้ที่หน้าของเรา ทางเลือกอื่นสำหรับ OpenVPN แนะนำ.
⚔️ เปรียบเทียบ OpenVPN
Here is how OpenVPN stacks up against each competitor:
- OpenVPN vs Nordvpn: Nord wins on speed and setup time. OpenVPN wins if you want the server under your own roof.
- OpenVPN เทียบกับ ExpressVPN: Express is easier for travel. OpenVPN costs nothing once your box runs.
- OpenVPN เทียบกับ PureVPN: PureVPN is cheaper per month. OpenVPN gives full control of logging and keys.
- OpenVPN vs SurfsharkVPN: เซอริฟชาร์ก covers unlimited devices. OpenVPN covers unlimited devices too, if you self-host.
- OpenVPN เทียบกับ ProtonVPN: Proton is the better ready-made privacy vpn service. OpenVPN is the better toolkit.
- OpenVPN เทียบกับ PrivadoVPN: Privado wins on price alone. OpenVPN wins on transparency and ตรวจสอบ เส้นทางเดินป่า
- OpenVPN เทียบกับ CyberGhost: CyberGhost is built for streaming. OpenVPN is built for infrastructure.
เริ่มใช้งาน OpenVPN ได้เลย
คุณได้เรียนรู้วิธีการใช้งานฟีเจอร์หลักๆ ของ OpenVPN แล้ว:
- ✅ การเข้าถึงระยะไกลที่ปลอดภัย
- ✅ การสื่อสาร IoT ที่ปลอดภัย
- ✅ Create Secure Access to SaaS Applications
- ✅ การเชื่อมต่อเครือข่ายระหว่างไซต์
- ✅ Enforce Zero Trust Access
- ✅ DNS Security and Content Filtering
- ✅ การป้องกัน SaaS
ขั้นตอนต่อไป: เลือกฟีเจอร์หนึ่งอย่างแล้วลองใช้ดูเลย
คนส่วนใหญ่มักเริ่มต้นด้วยการตั้งค่าการเข้าถึงระยะไกลที่ปลอดภัย (Secure Remote Access)
ใช้เวลาน้อยกว่าห้านาที
ถาม บ่อย ๆ
ฉันจะใช้ OpenVPN เป็น VPN ได้อย่างไร?
Install the openvpn client, import an ovpn file from your vpn provider, then connect. All traffic then travels inside an encrypted tunnel to the vpn server.
ฉันจะเริ่มต้นใช้งาน OpenVPN ได้อย่างไร?
On Windows, launch the OpenVPN GUI as administrator and pick your profile from the system tray applet. On Linux, run sudo systemctl start openvpn@server.
ฉันสามารถใช้ OpenVPN ได้ฟรีหรือไม่?
Yes. The community edition is free and open source. Access Server is also free for three simultaneous client connections, which covers most home setups.
วิธีใช้งาน OpenVPN ใน Windows?
Install openvpn software, copy your .ovpn configuration file into the config folder inside Program Files, then right-click the tray icon and choose Connect.
VPN กับ OpenVPN ต่างกันอย่างไร?
A VPN is the general idea of a private tunnel. OpenVPN is one specific openvpn protocol and program that creates that tunnel using SSL/TLS.
 English
 Spanish
 Chinese
 German
 French
 Arabic
 Russian
 Portuguese
 Japanese
 Korean
 Italian
 Turkish
 Dutch
 Polish
 Indonesian
 Thai
 Vietnamese